
Smarter by Design.Simpler for Business
Dashboard
What Is Dashboard?
Dashboard is the tab that shows the session, authentication, lockout, multi-factor authentication, system and bot metrics of a vService with the AGS access control enabled on a multi-panel monitoring screen with a selectable time range. When the AGS-Enabled vService management screen is opened, the Dashboard tab (with the name of the vService) comes first; while the dashboard is open, when another vService is selected from the list the tab open at that moment is preserved.
The screen gathers in different panels data such as the number of concurrent sessions, the success and error distribution of the authentication attempts, the attempts on the basis of the provider, the active lockouts and the lockout scopes, the CAPTCHA, TOTP and OTP verification counters, the separation of the requests by AGS as authorized or unauthorized, the storage and memory usage of the AGS engine and the bot score distribution. Every panel can be displayed in the form of a graph, a table, a pie or a counter; it is updated automatically according to the selected time range. A brute force attempt or a login problem caused by a provider is noticed immediately: in which provider the failed attempts are piling up, in which scope the lockouts are opened and how the number of sessions changes are seen on a single screen.
All monitoring capabilities are a built-in part of TR7: data is collected on the device with per-second resolution and stored in archives of up to 10 years; without the need to install an external analytics or SIEM tool, trends from years ago can be examined retrospectively in addition to real-time monitoring. Archiving is tiered: the finest resolution is kept only for the recent past, and as data ages it is stored summarized in wider steps.
1 s
Data Collection per Second
Metrics are collected with per-second resolution; panels are updated automatically according to the selected range
10 Years
Historical Data
Statistics are stored in archives of up to 10 years; the time range picker offers preset ranges of up to 5 years
Built-in
No External Tool Needed
All data is collected on the device; no separate analytics/SIEM installation is required
6
View Tabs
All six are displayed unconditionally in every AGS-enabled vService
14
Preset Time Ranges
Preset ranges from 5 minutes to 5 years; also free duration and date range input
33
Different Panels
30 AGS panels and 3 bot panels in common with the Bot/DDoS dashboard
HTTP
vService Type
Since AGS is enabled only in the HTTP vServices, the dashboard opens only in this type as well
32
Panels per Tab
At most 32 panels per view tab, at most 16 custom templates per user
Personal
Customizable Layout
Templates, adding/moving panels and resizing are stored per user
Accessing Dashboard
- Left Monitor Panel is opened.
- AGS-Enabled vServices is selected from the category tabs at the top left.
- The vServices defined on TR7 with AGS access control enabled are listed.
- The vService to be monitored is clicked; the screen opens with the Dashboard tab that carries the vService's name.
Only the vServices of the HTTP type whose AGS is on are located on the list. Every row carries the Actions (the summary with icons of the chain of steps the visitor has passed; the names of the steps are displayed in the tooltip of the cell) and Portal Applications (the number of applications the portal publishes) information of the vService; the primary metric of the row is AGS Concurrent Sessions. The status color in the row is not the running state of the vService but of the AGS engine: running is shown green; starting and partially degraded yellow; not responding, restarting repeatedly (crash loop), stopped and not created red; if the engine state has not been reported yet, the row is seen gray with the text unknown. In cluster setups the worse state of the two devices is shown. The list is listed by default in ascending order by the vService name and is filtered by the name or by the state; the state filter works according to the combined state of the vService.
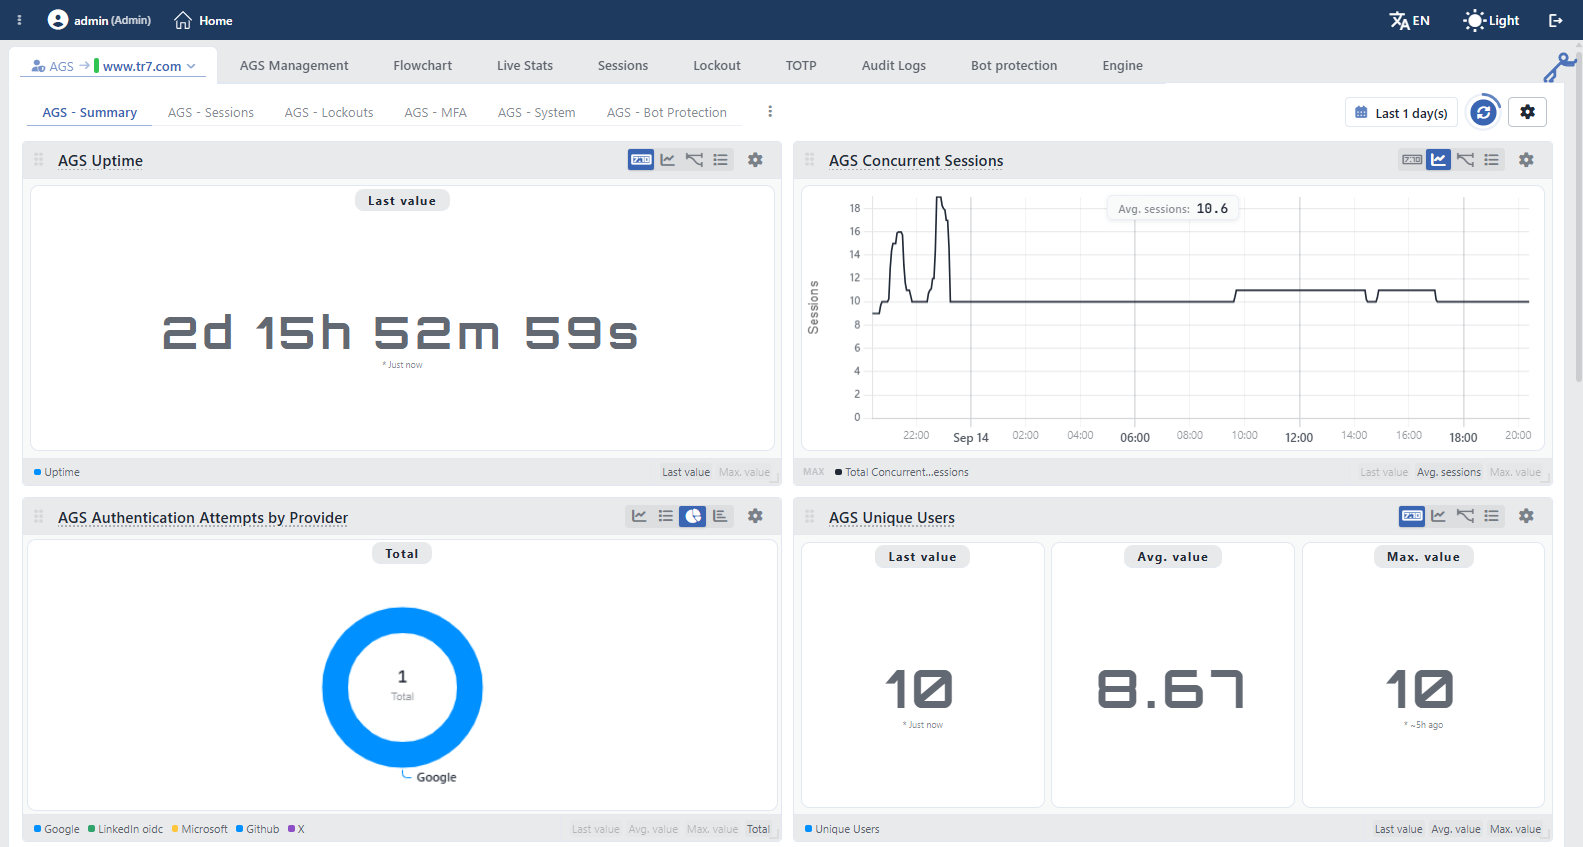 AGS Dashboard
The Tab Bar
Next to the Dashboard tab, the AGS Management, Flowchart, Live Stats, Sessions, Lockout, TOTP, Audit Logs, Bot Protection and Engine tabs are located on the same screen. The tabs other than Bot Protection are always present. Bot Protection, on the other hand, is displayed only if at least one of the bot protection policies of the vService is triggered by request or failed login counting or if its action is Block. There is no separate authorization condition in the tabs.
The label of the first tab is in the form AGS → <vService name>; the colored strip before the name carries the status color of the AGS engine. The down arrow at the end of the label opens the menu for passing to the Load Balancer Dashboard, WAF Dashboard (if WAF is enabled in the vService and the user has WAF permission) and Bot/DDoS Dashboard (if Bot/DDoS is enabled in the vService) dashboards of the same vService. The first row of the menu is the AGS dashboard that is open, with a check mark; in the other rows the status color of that module is located before the name of every dashboard. While the tab is already selected, the whole of the label opens this menu as well. Since the Load Balancer dashboard is always listed, the menu is always present on this screen. Unlike the Load Balancer dashboard, there is no ⋮ menu at the right end of the tab bar. The open tab is written to the address bar and is shared by copying the link.
On the right side of the screen there is also a collapsible panel that summarizes the AGS configuration of the vService as an access flow diagram; its detail is located in the AGS - AAM Data Flow Panel section.
AGS - AAM Data Flow Panel
The preview panel on the right side of the screen summarizes the AGS configuration of the vService as an access flow diagram. The panel has no separate title in the interface; in this document it is explained under the name AGS - AAM Data Flow Panel so that it can be referred to easily. For the introduction of the panel see AGS - AAM Data Flow Panel. In the diagram, the path the traffic follows from entering through the listener addresses, passing through the AGS gate, the login flow, the protection and session policies, until it concludes at the decision node and reaches the Backend Services is seen at a glance. Every element in the diagram reflects the live configuration; with the gear icons of the cards the editing window of the AGS setting in question opens, and on the Sign-in Flow card the Flowchart tab in the editing mode.
The panel is seen only on the Dashboard and AGS Management tabs; when it is passed to the other tabs it closes. It is collapsed and expanded by clicking the handle figure outside the left of the panel; when it is hovered over, the figure shows the opposite operation. The resizing is done only by dragging from the left edge of the panel. Unlike the Load Balancer dashboard, the collapsing handle carries not the status color of the vService but the accent color of the theme. The width and the collapsed state are remembered per user. The panel has no closing button; it can only be collapsed.
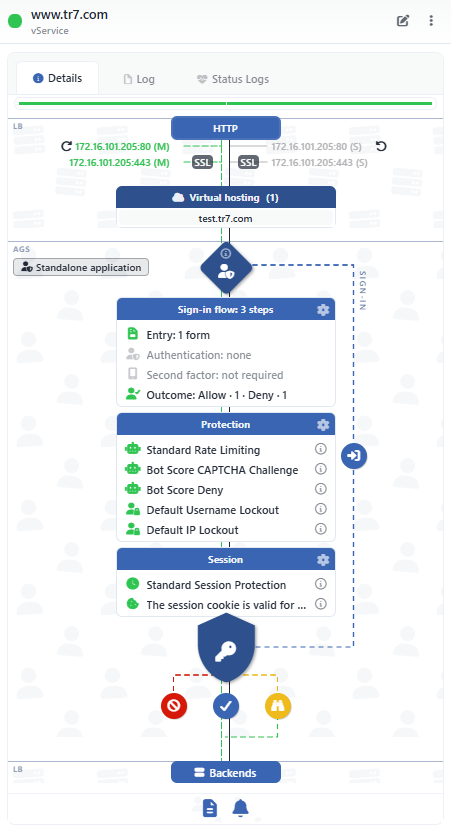 AGS - AAM Data Flow Panel
The diagram is dynamic
The AGS - AAM Data Flow Panel is not a fixed image; it is shaped dynamically according to the AGS configuration of the vService. The titles and the rows of the cards, the colored or faded appearance of the rows, the result strips below the decision node, the SIGN-IN path and whether a fourth card is present depend entirely on the settings at that moment: for example if there is no provider in the login flow the Authentication row is seen faded, if there is no step in the flow the SIGN-IN path is not displayed at all, and if there is no bot policy whose action is showing a CAPTCHA, showing a content page or limiting the bandwidth the yellow Challenged strip is not displayed. In this panel only the AGS layer is shown; the WAF and Bot/DDoS strips together with the certificate, rule, cache and distribution cards of the Load Balancer are not located in the diagram.
The image above shows an example vService that works in the Standalone Application mode, whose login flow consists of a form together with the Allow and Deny steps, and in which three bot protection policies and two default lockout policies are defined. The explanations on this page cover all the elements that can be seen in the diagram and under which condition they are seen; the diagram on the screen can be different from this example according to the configuration of the vService.
Panel Header
In the title there are the name of the vService, the vService subtitle below the name and the colored status dot that shows the combined state: green OK, red Error, orange Warning, blue Evaluating, gray Disabled. In cluster setups the dot is in two halves; the left half shows the state of this device and the right half that of the peer device.
At the top right there are a shortcut and a menu. The shortcut is shown only as an icon; its name is seen when it is hovered over. Edit is displayed only in the users who have the change authorization in the Load Balancer area.
| Button | Function |
|---|---|
| Edit | It is passed to the Flowchart tab and the flow diagram opens in the editing mode. On the Flowchart tab the preview panel closes. |
In the ⋮ menu next to it there is a single operation: Restart Engine. The operation restarts the AGS engine of the vService only on this device after the "Are you sure?" confirmation and is written to the audit record. The operation requires the Load Balancer change authorization. The tcpdump, Delete, Reload, Enable and Disable operations on the Load Balancer dashboard are not in this menu.
Panel Tabs
| Tab | Content |
|---|---|
| Details | The status strip, the configuration warnings, the device based status messages and the flow diagram below them. The thin color strip right below the tabs shows the combined state of the vService on that device (green = OK); in a cluster a separate strip is displayed for every member. If there is an error in the configuration, the number of errors and the categories are summarized in a single warning row. If there is a configuration that has been withdrawn from use, a warning row is displayed as well; the status messages are shown at most in four rows per device, and the rest are behind an opening row. |
| Log | The ones with the AGS label among the audit (who changed what, when) records of the vService: the creation, editing and deletion of the AGS records, the revoking of a session, the clearing of a lockout and of the failed attempts, the deletion of a TOTP record, the restarting of the engine and the cleaning of its storage, the password operations. They are listed with the date range, record limit, refresh and Excel/CSV export tools; with a separate icon the records are opened in the full screen log view. |
| Status Logs | The state transition history of the vService; every transition is listed with the "old state → new state" badges and a justification row. It is filtered with the date range and limit selection, and there is a refresh button. The encrypted support bundle rows produced for diagnostics purposes are seen here as well and can be downloaded. |
The Flow Diagram: The LB Section
The upper section of the diagram is marked with the LB strip and shows the entry layer of the vService. In this panel the Load Balancer section consists only of the entry elements:
| Element | Meaning |
|---|---|
| The Type Node | The blue node at the very top shows the type of the vService. Since AGS is enabled only in the HTTP vServices, the node always reads HTTP in this panel. The node is not clickable. The Debug mark on the Load Balancer dashboard is not displayed in this panel. |
| The Listener Rows | Every row is a listener address (IP:port). In cluster setups the left side of the row shows the instance on this device and the right side the instance on the peer device; in the cluster (VIP) type IPs, (M) states the master and (S) the slave instance. The color is the running state of the address on that device; the addresses turned off manually are also shown struck through. When the address is clicked, the IP detail window opens; with the copy icon that appears when the row is hovered over, the full link form of the address is taken to the clipboard. |
| The SSL Badges | In the listeners on which the SSL termination is done, the SSL badge is displayed next to the address; in the listeners on which QUIC (HTTP/3) is enabled, h3 is added next to the badge. In the listeners that redirect from HTTP to HTTPS, on the other hand, the Redirect SSL mark in the form of a circular arrow is shown. |
| Virtual Hosting (N) | It is displayed if at least one virtual domain name is defined. The number in the title is the number of defined domain names; the domain names are listed below it. Four domain names are shown by default; the number of the rest is stated in the ... N more row and the list is opened with the down arrow in the title; when the title is hovered over, all of the domain names are displayed. |
The Flow Diagram: The AGS Section
The AGS strip contains the path the traffic follows in the access control layer and the AGS configuration cards. The cards are placed in a fixed order: the gate node, Sign-in Flow, Protection, Session and, in the portal modes, a fourth card. In this panel AGS is shown in the detailed view (if the AGS configuration record of the vService has not been created yet, only an AGS badge that is not clicked is displayed); the eye icon that provides the summary/detail transition on the Load Balancer dashboard is not present.
| Element | Meaning |
|---|---|
| The Mode Badge | Below the strip label, the badge that shows the working mode of AGS is always displayed: Standalone Application (the vService stands in front of a single application, the users open a session directly here), Portal (the users open a session here and reach the published applications from here) or Portal Application (the application does not offer its own login pages, it takes over its session from a trusted portal). The badge is not clickable. |
| The Gate Node | It is the diamond node that represents the entry gate to AGS. With the information icon on it a summary window opens: the sentence of the mode, which requests pass through AGS (if no condition is defined, Every request to this vService goes through AGS), the path on which the login and verification pages are served (by default /ags-portal) and, in the portal mode, the portal address. In the users who have the editing authorization there is an Edit button in the window; the Scope & Identity window opens. |
| Sign-in Flow: N Steps | The card that summarizes the login flow. The number in the title is the total of all the steps in the flow (the form, provider, multi-factor authentication, user information assignment, Allow, Deny and branch steps); if there is a branch in the flow, the number of branches is added to the title as well. The rows are located in the table below. The gear icon opens the Flowchart tab in the editing mode. If the flow has not been built yet, the number of steps is not located in the card title and only the row "The sign-in flow is not built yet — it is created in the flow editor" is displayed faded on the card. |
| Protection | It lists the Bot Protection Policies and the default Account Lockout Policies policies assigned to the vService. The bot policies are shown with a robot icon, the lockout policies with a locked user icon, with the policy names and in the order of assignment. With the information icon in the row, the trigger and action sentence of the policy (e.g. Requests with a bot score of 80 or above → deny) or the lockout levels are displayed. If there is no bot policy, the row No bot protection policy is set, and if there is no lockout policy, the row "No default lockout policy — authentication providers may use their own" is displayed faded. The gear icon opens the Protection editing window. |
| Session | It consists of two rows. The first row is the name of the assigned Session Protection Policies policy; if no policy has been selected, the row is displayed faded. With the information icon, the sentences of what the session is bound to, the idle and absolute timeouts and the concurrent session limit are displayed. The second row shows the area in which the session cookie is valid; if the cookie area is not defined, it writes The session cookie is valid for this address only. The gear icon opens the Session editing window. |
| Portal & Applications | It is displayed only in the Portal mode. Every published application is a row; the applications for which no target vService has been selected are shown faded. If there is no application, the row No applications are published yet is displayed. |
| Trusted Portals | It is displayed only in the Portal Application mode. Every portal whose session is trusted is a row; if the list is empty, a single faded row is displayed on the card. |
The rows of the Sign-in Flow card:
| Row | Meaning |
|---|---|
| Entry | It shows the number of forms in the flow (Entry: 1 form); the steps that use the same form profile are counted as a single form. If there is no form in the flow, the row is not displayed at all. |
| Authentication | It shows the number of Authentication Providers in the flow; with the information icon the names of the providers are listed. If there is no provider, it writes Authentication: none and the row is displayed faded. |
| Second Factor | It shows the names of the Multi-Factor Authentication (MFA) steps in the flow; if there are more than two, the rest are added as +N. If there is no MFA, it writes Second factor: not required and the row is displayed faded. |
| Outcome | It shows the number of the Allow and Deny steps in the flow (Outcome: Allow · 1 · Deny · 1). If neither is present, it writes Outcome: none and the row is displayed faded. |
The status icon in the rows is shown green in the active rows and gray in the faded rows.
The editing is done only from the card gear
There is no editing button in the row information windows; the editing is done from the window opened with the gear icon of the card. The gear icons of the cards are displayed only in the users who have the vService editing authorization; in the AGS cards there is no + button and no collapsing arrow as on the Load Balancer dashboard.
The Flow Diagram: The Decision Node and the Flow Paths
| Element | Meaning |
|---|---|
| The Decision Node | The shield with the key symbol below the cards is the decision point of AGS: every request that passes the access control is concluded here. The node is always displayed and is not clickable. Below it, at most three result icons appear according to the configuration; the results are determined only according to the action types and are not affected by the policy conditions. |
| Denied | The red prohibition icon on the left. It is displayed if there is a Deny step in the flow, at least one default lockout policy or a bot policy whose action is deny, tarpit or block. The path of the refused request ends here; there is no return line to the main path. |
| Signed In | The blue check icon in the middle. It is displayed if there is at least one step in the flow; it shows that the request carrying a valid session continues to the Backend Service. It is not a separate strip, its icon stands directly on the main path. |
| Challenged | The yellow binoculars icon on the right. It is displayed if there is at least one bot policy whose action is showing a CAPTCHA, showing a content page or limiting the bandwidth. The icon means not monitoring but a challenge: a CAPTCHA or a content page is offered to the visitor. The strip joins back to the main path with a green return line. |
| The SIGN-IN Path | It is the dashed path in the accent color, displayed if there is at least one step in the flow, that goes out from the gate alignment to the right edge and returns to the decision node. The login icon on it shows that the visitor who has no session is directed to the login flow. The path and the icon are not clickable. |
| Backends | The single node located in the LB strip at the end of the diagram represents the Backend Services the traffic that passes the access control reaches. In this panel the Backend Services are not listed as separate boxes; the node is not clickable. |
Bottom Settings Strip
The icon strip below the diagram represents the AGS settings that are not shown as a separate card on the traffic path. When an icon is clicked, the summary window of the section in question opens; in the window there is a Go to Page button and, in the users who have the editing authorization, an Edit button. Both icons are always displayed in color independently of whether the setting is filled or empty; whether a setting is defined cannot be understood by looking at the appearance of the strip.
| Icon | Section |
|---|---|
| Presentation & Language: the languages in which the pages are served, the number of customized texts and the browser tab title. In the editing window there are the Page Templates and Dictionaries (Multilingual) selections. | |
| Monitoring & Notification: the notification profile, the targets to which the audit record is forwarded and (if it is outside the default) the log level. In the editing window there are the Notification Profiles, Log Forwarding and log level selections. |
Since the session and protection settings are shown as a card each on the traffic path, they are not repeated on this strip.
View Levels (Drill-Down)
The AGS monitoring view is offered at two levels:
| Level | Scope |
|---|---|
| All vServices | The AGS tab on the Home screen of the device; on the Sessions, Lockouts and MFA subtabs it shows the collective panels (with the All vServices - prefix) that cover all the AGS-enabled vServices. On the Sessions subtab there is also the AGS Concurrent Sessions panel with the vService breakdown (with the - vService Distribution suffix). Its detail is located on the AGS page. |
| vService | The AGS Dashboard of a single selected vService (the screen explained on this page). |
This page describes the Dashboard at the vService level; the panels on this screen show only the selected vService's data.
In addition, when a time range is selected by dragging horizontally over the panels, the whole dashboard is locked to that range. Because this selection produces an absolute start/end range, it also stops automatic refresh; to return to a relative range, a preset range is selected from the time range picker.
Screen Controls
Above the panels there is a full width toolbar that controls all the panels together. On the left of the bar there are the view tabs and the template menu; on its right the time range selector, the refresh button and the settings. In the top right corner of every panel, on the other hand, there are the view icons specific to that panel. The report shortcut on the WAF dashboard and the view mode setting on the Bot/DDoS dashboard are not on this dashboard.
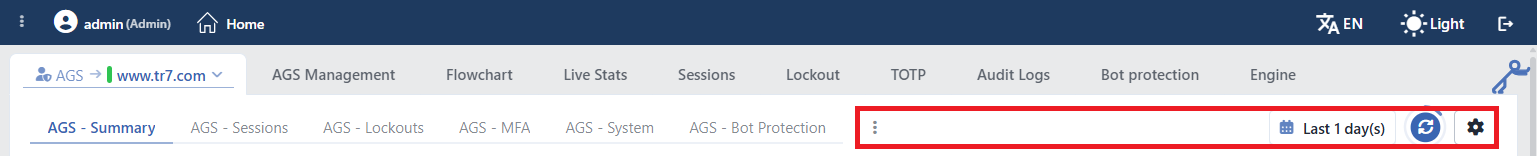 The Screen Controls
INFO
Menu
The menu at the end of the view tabs contains the operations for the Dashboard tab layouts (templates). When a view tab is double-clicked, that template is returned to its default state; the operation again requires confirmation.
Create New Template
A new empty template (tab layout) is created. In the window that opens, the template is given a name, and the template opens as soon as it is created.
Duplicate Current
A copy of the current template is created; the copy is given a new name. The option is enabled only while a template is open.
Edit Template
The name of the current template is edited. The option is enabled only for templates created by the user; it is inactive for preset templates. The layout is not changed from this window; panels are edited by dragging and resizing them directly.
Reset to Default
The current template is returned to its default state after confirmation is obtained. The option is enabled only for templates on which changes have been made.
Remove Template
The current template is deleted after the confirmation is taken. The option is active only in the templates the user has created; the built-in templates cannot be deleted. When the tab of a user template is clicked with the middle mouse button, it is deleted with the same confirmation as well.
Reset All to Defaults
After confirmation is obtained, the dashboard is returned entirely to its default state: the templates created by the user are deleted, the panel changes in preset templates are undone, and the toolbar preferences (time range, automatic refresh, resolution, source, height, theme) return to their default values.
INFO
Last 1 day(s) Time Range
Which time slice the panels will show the data of is selected; the default range is Last 1 day(s). The preset ranges are fourteen and extend from 5 minutes (Last 5 minute(s)) to 5 years (Last 5 year(s)): 5 minutes, 15 minutes, 30 minutes, 1 hour, 3 hours, 12 hours, 1 day, 3 days, 7 days, 1 month, 3 months, 6 months, 1 year and 5 years. Next to the preset ranges, a free duration (minute, hour, day, week, month, year) is entered with Custom Duration. All the panels are updated according to the selected range. When the dashboard is opened from the Left Monitor Panel, the duration selected in the panel is applied as the time range. The selection made is stored per user and is preserved in the following sessions.
An absolute range can also be selected by entering a start and end date in the Custom Date Range section.
An absolute range stops automatic refresh
In ranges selected by entering a start/end date, the panels do not refresh by themselves; the data is refreshed only with the refresh button. In addition, an absolute range is not stored as a user preference; when the screen is reopened, it returns to the relative range.
INFO
Refresh
Reloads the data in the panels instantly; the button becomes inactive while loading is in progress. Automatic refresh is enabled by default and the panels update by themselves every 10 seconds; the remaining time is shown with the progress ring around the button. On refresh, the cache is bypassed and the panels are loaded in sequence in groups of twenty.
INFO
Settings
The Dashboard general view and the display settings of the panels are accessed. The window is divided into three sections: Data (resolution and automatic refresh), Clustering (source selection; only while the cluster is enabled) and Visual (height and theme).
Chart Resolution
The resolution of the charts (data point density) is selected: High Resolution (1,440 points), Standard Resolution (720 points, default) or Low Resolution (360 points). High resolution provides a more detailed display, and low resolution a more performant one.
Auto-Refresh
The automatic refresh interval of the panels is set: Disabled, 5s, 10s, 30s and 60s. The default value is 10 seconds.
Source
In cluster setups, which member's data is shown is selected. The options are this device's name, the peer device's name and Both Devices; the default is Both Devices. This section is displayed only while the cluster is enabled.
Height
The height of the panels on the screen is set.
Theme
The display theme (color scheme) of the charts is selected: Professional (default), Corporate, High Contrast, Monochrome Blue and Colorblind Safe.
INFO
Panel View Icons
With the icons in the top right corner of every panel, the display form of the data is changed. The icons are displayed only if more than one view is offered in the panel; in a panel only the views suitable for that data are active. For example the pie chart is offered only in the distribution panels and the heat map only in the bot panels.
| Icon | View | What does it do? |
|---|---|---|
| Line Chart | It shows the change of the metric over time (its trend); in the panels with many series it is shown stacked. | |
| Bar Chart | Compares the values between series with side-by-side bars. | |
| Pie Chart | Shows the proportional share of the series within the total. | |
| Heatmap | Shows the series as color bands on the time axis; as density increases, the band "heats up". | |
| Stat Table | Lists the series in a sorted table with their summary values (last/average/highest/total); clicking a column header sorts by that column. | |
| 7:10 | Digital | Highlights summary values with large digits. A separate section is shown for each summary that is on, and a separate row for each series; a single large value display appears only in panels that have a single series and show a single summary. |
| Mini Chart | Shows the metric as a compact trend curve (summary card). |
The Mini Chart view is added by itself to every panel that has a single series and offers the line view.
The settings specific to the panel in question are reached from the symbol of the panel. The panels are moved by being dragged from the handle in their title (not from anywhere on the card) and are resized from their bottom right corner; a new panel is added to the tab with the Add Visualization card at the end of the layout. When the panel title is hovered over, the explanation that tells what the panel measures is displayed as a tooltip. All the layout changes made are stored specially for the user.
INFO
Panel Metric Columns
Below each panel, the summary statistics of that metric are listed in columns for each series shown:
| Column | Meaning |
|---|---|
| Last value | The last (most recent) value in the selected range |
| Avg. value | The average value over the range |
| Max. value | The highest value in the range |
| Total | The total accumulated over the range |
The name of the open summaries carries the unit of the metric; the closed summaries are seen on the strip with their general name (Last value, Avg. value, Max. value, Total). The names with the unit attached are as follows: Last sessions, Avg. sessions and Max. sessions in the concurrent session panels; Avg. ses/s and Total sessions in the session creation and authentication panels; Avg. req/s and Total requests in the AGS Authentication and AGS Request Distribution panels; Avg. evt/s and Total events in the lockout event, CAPTCHA, TOTP, OTP and audit panels. The AGS Uptime, AGS Unique Users, AGS Active Lockouts, AGS Active Lockouts by Scope, provider distribution, storage and memory panels carry the general names; AGS Uptime offers only the Last value and Max. value summaries.
Which summaries are present changes according to the type of the metric: Total is present only in the rate metrics; in the instantaneous (gauge) panels Last value, Avg. value and Max. value are offered (AGS Uptime offers only Last value and Max. value). Which of the present summaries come open by default, on the other hand, changes according to the view:
- The Stat Table view lists all of the existing columns.
- The line and bar views show only Total in rate metrics and only Avg. value in gauge metrics.
- In the Digital view it changes according to the panel: AGS Uptime only Last value; AGS Concurrent Sessions, AGS Unique Users and AGS Active Lockouts the last, average and highest values; AGS Sessions Created, AGS Sessions Authentications and AGS Lockout Events only the total.
- In the pie view only Total comes open in the provider distribution panels.
Disabled summaries are enabled by clicking them in the strip below the panel. By clicking the series names in the same strip, individual series are also hidden and shown.
The summary strip does not appear in the line view of multi-series panels
The summary boxes are opened in the line view only if there are at most six series in the panel. For this reason, when the provider distribution panels of a vService in which a large number of providers are defined are passed to the line view, no summary is shown. The bar, pie and table views are not affected by this threshold; the summaries are read from these views.
View Tabs
The Dashboard contains upper tabs that group the panels according to their subjects. By default the AGS - Summary tab comes open; if another tab has been selected before within the same navigation, that tab is remembered. The open tab is written to the address bar.
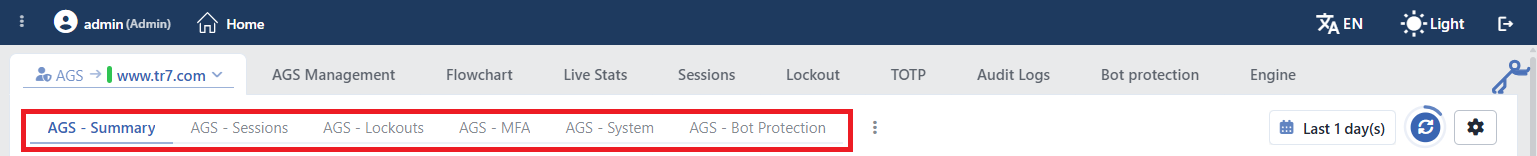 The View Tabs
| Tab | Visibility Condition | Content |
|---|---|---|
| AGS - Summary | Always | The summary view selected from the uptime, session, authentication, lockout, verification, request and audit panels. |
| AGS - Sessions | Always | The session, authentication and request distribution panels. |
| AGS - Lockouts | Always | The active lockouts, the lockout events and the lockout scope breakdowns. |
| AGS - MFA | Always | The CAPTCHA, TOTP and the e-mail, SMS and custom channel OTP panels. |
| AGS - System | Always | The storage, memory, audit record and uptime panels of the AGS engine. |
| AGS - Bot Protection | Always | The bot score, score class and detection factor distribution panels. |
The tab and the panel being seen does not mean that the data is produced
All six tabs are displayed in every AGS-enabled vService. The great majority of the panels also depend only on AGS being on in the vService: for example in a vService in which no e-mail, SMS or custom channel OTP has been configured, the OTP panels on the AGS - MFA tab are still displayed and show a zero value. There are only two panels that are not created at all when their condition is not met: AGS Authentication Attempts by Provider (if there is no authentication provider in the flow) and AGS CAPTCHAs Shown by Provider (if there is no CAPTCHA provider in service).
The same panel can be located in more than one tab; below, each panel is described in detail only in the tab where it first appears, and its repetitions are linked to the related description.
AGS - Summary Tab
The AGS - Summary tab gathers the basic panels that summarize the general state of AGS. The panels on this tab have been selected manually and all of the eleven panels are located on another view tab as well. If there is no authentication provider in the flow, there are ten panels on the tab.
AGS Uptime
It shows the uninterrupted uptime of the AGS engine of the vService (the Uptime series). As a summary only Last value is printed; the value is shown in a readable form such as 2d 15h 52m 59s. The time being reset shows that the engine has restarted; the value staying at zero, on the other hand, means that the engine is not running or is not responding. In the moments when the session store cannot be accessed, a gap occurs in the graph. In cluster setups the time of every device is shown as a separate series, they are not added up.
AGS Concurrent Sessions
It shows the total number of sessions open in AGS at that moment (the Total Concurrent Sessions series). In this view Avg. sessions is printed as the summary. The panel is the default primary metric of the AGS-Enabled vService rows in the Left Monitor Panel.
AGS Authentication Attempts by Provider
It shows how the authentication attempts are distributed among the providers: every Authentication Providers profile in the flow is a series and the series name is the name of the profile. The value is the number of attempts that reach the provider; the success, failure and error breakdown of the attempts is read from the AGS Authentication panel. In the pie view only Total is printed as the summary. When a provider is renamed, the series name is refreshed and the historical data is preserved. The series are ordered according to the system identity of the provider profiles; the series of a provider removed from the flow is not shown on the panel.
The panel is displayed only if there is a provider in the flow
This panel requires at least one authentication provider step to be present in the login flow of the vService. If there is no provider step, the panel is not created.
AGS Unique Users
It shows the number of unique users whose identity has been verified (the Unique Users series). As a summary Last value, Avg. value and Max. value are printed in three separate sections.
AGS Authentication
It shows the authentication operations in four series: Attempts, Success, Failed and Errors. In the table view all of the Last req/s, Avg. req/s, Max. req/s and Total requests columns are listed. The share of the failed attempts within the attempts growing is the first indicator of a brute force or a credential stuffing attempt.
AGS Active Lockouts
It shows the number of lockouts active at that moment (the Active Lockouts series). As a summary the last, average and highest values are printed. In which scope the lockouts have been opened is read from the AGS Active Lockouts by Scope panel.
AGS Lockout Events
It shows the lockout events in two series: Created (the newly opened lockouts) and Blocked (the requests blocked because of a lockout). As a summary Total events is printed.
AGS CAPTCHA
It shows the CAPTCHA verification in four series: Shown, Answered, Correct and Incorrect. Answered is the total of the correct and incorrect answers. The panel is displayed even if no CAPTCHA has been configured. The table, line and bar views are offered; there is no digital view.
AGS OTP Verification (All Channels)
It shows the one-time code verifications of all the verification channels (e-mail, SMS, custom channel and TOTP) together: Shown, Answered, Correct and Incorrect. The separation on the basis of the channel is read from the channel panels on the AGS - MFA tab.
AGS Request Distribution
It shows the distribution of the requests that come to the vService according to the AGS authorization state in three series: Authorized (authorized with a valid session), Unauthorized (having no valid session; including the login page requests) and Whitelisted (not passing the access control because it does not meet the AGS scope condition; if no scope condition is defined it stays zero). The series are shown stacked and as a summary Total requests is printed. The data of this panel is read not from the AGS engine but from the request counters of the load balancer; for this reason it continues to produce data in the moments when the session store of the engine cannot be accessed as well.
AGS Audit Events
It shows the rate of the audit record events AGS produces (the Events series). As a summary Total events is printed. The records themselves are listed on the Audit Logs tab.
AGS - Sessions Tab
The AGS - Sessions tab gathers the session life cycle, the authentication results and the request distribution. If there is an authentication provider in the flow, there are eight panels on the tab.
The repeated panels located on this tab (their explanations are located on the AGS - Summary tab):
- AGS Concurrent Sessions: it has been placed here as a digital value; the last, average and highest number of sessions are printed. See AGS Concurrent Sessions.
- AGS Authentication Attempts by Provider: see AGS Authentication Attempts by Provider.
- AGS Unique Users: see AGS Unique Users.
- AGS Authentication: see AGS Authentication.
- AGS Request Distribution: see AGS Request Distribution.
AGS Concurrent Sessions Breakdown
It shows the distribution of the open sessions as authenticated and unauthenticated in two series: Authenticated and Unauthenticated. The unauthenticated sessions belong to the visitors who have not completed the login flow yet; this series growing rapidly compared to the authenticated sessions points to heavy and inconclusive traffic directed at the login page.
AGS Sessions Created
It shows the number of new (not yet authenticated) sessions opened per second (the Created series). As a summary only Total sessions is printed.
AGS Sessions Authentications
It shows the number of sessions that complete their authentication per second (the Authenticated series). As a summary only Total sessions is printed. When it is read together with the AGS Sessions Created panel, how much of the sessions opened turn into a login is seen.
AGS - Lockouts Tab
The AGS - Lockouts tab shows the effect of the Account Lockout Policies policies. There are five panels on the tab. In the three panels with the scope breakdown, every lockout scope is a series:
| Series | Scope |
|---|---|
| Username | The lockouts of the policies whose Policy Scope value is Username Only |
| Username + IP | The lockouts with the Username + IP scope |
| IP Address | The lockouts with the IP Address Only scope |
| Composite | The lockouts with the Custom Combination scope |
The four series are located on the panel and show a zero value even if there is no policy with the scope in question in the vService.
The repeated panels located on this tab (their explanations are located on the AGS - Summary tab):
- AGS Active Lockouts: it has been placed here as a line chart. See AGS Active Lockouts.
- AGS Lockout Events: it has been placed here as a digital value; only Total events is printed. See AGS Lockout Events.
AGS Active Lockouts by Scope
It shows the distribution of the active lockouts according to the scope. In the table view the last, average and highest value are listed for every scope.
AGS Lockouts Created by Scope
It shows the rate of the newly opened lockouts according to the scope. In the table view the Last evt/s, Avg. evt/s, Max. evt/s and Total events columns are listed. Whether the attack is directed at the user names or at the source addresses is read from this panel.
AGS Lockouts Blocked by Scope
It shows the rate of the requests blocked because of a lockout according to the scope. Its columns are the same as those of the AGS Lockouts Created by Scope panel.
AGS - MFA Tab
The AGS - MFA tab shows the verifications made with a CAPTCHA and a one-time code on the basis of the channel. If there is a CAPTCHA provider in service, there are eleven panels on the tab. In the code sending panels there are three series: Sent, Resent and Send Errors. In the code verification panels there are four series: Shown, Answered, Correct and Incorrect.
The repeated panels located on this tab (their explanations are located on the AGS - Summary tab):
- AGS CAPTCHA: see AGS CAPTCHA.
- AGS OTP Verification (All Channels): see AGS OTP Verification (All Channels).
AGS CAPTCHAs Shown by Provider
It shows the distribution of the CAPTCHAs shown among the CAPTCHA Providers profiles: every provider profile is a series. The correct and incorrect answer breakdown is read from the AGS CAPTCHA panel. In the pie view only Total is printed as the summary.
The panel is displayed only if there is a CAPTCHA provider in service
A provider comes into service in two ways: a lockout policy whose CAPTCHA protection is on and whose attempt threshold is defined (the default lockout policies or the lockout policies of the provider and MFA steps themselves) or a bot protection policy whose action is to show a CAPTCHA. If neither is present, the panel is not created.
AGS TOTP
It shows the time-based one-time password (TOTP) verifications. The management of the TOTP records is done on the TOTP tab.
AGS Email OTP Sending
It shows the one-time codes sent over the e-mail channel. In the bar view only Total events is printed as the summary. The Send Errors series growing points to a problem in the e-mail sending configuration.
AGS Email OTP Verification
It shows the verifications of the codes sent over the e-mail channel.
AGS SMS OTP Sending
It shows the one-time codes sent over the SMS channel. Its summaries are the same as those of the AGS Email OTP Sending panel.
AGS SMS OTP Verification
It shows the verifications of the codes sent over the SMS channel.
AGS Custom OTP Sending
It shows the one-time codes sent over the custom channel.
AGS Custom OTP Verification
It shows the verifications of the codes sent over the custom channel.
AGS OTP Sending (All Channels)
It shows the e-mail, SMS and custom channel code sendings together. The separation on the basis of the channel is read from the channel panels on this tab.
AGS - System Tab
The AGS - System tab shows the resource usage of the AGS engine of the vService, the session store usage, the audit event rate and the uptime. There are six panels on the tab. The memory and uptime panels belong not to the whole of the device but to the AGS engine of that vService; Home & Dashboard is used for the device-wide view.
The repeated panels located on this tab (their explanations are located on the AGS - Summary tab):
- AGS Audit Events: it has been placed here as a digital value. See AGS Audit Events.
- AGS Uptime: it has been placed here as a line chart. See AGS Uptime.
AGS Storage Entries
It shows the total number of records the AGS engine keeps in its session store (the Entries series).
AGS Storage Memory
It shows the memory usage of the AGS session store (the Memory series).
AGS Container Memory
It shows the memory usage of the AGS engine in two series: Used and Available. Available is calculated by subtracting the used memory from the memory limit allocated to the engine. When the memory information of the engine cannot be read, both series stay empty. As a summary the average and the highest value are printed. In cluster setups the value of every device is shown as a separate series.
AGS Container Memory %
It shows the ratio of the memory usage of the AGS engine to the limit as a percentage (the Usage % series); the threshold coloring is applied. If the limit cannot be read, the panel stays empty. In cluster setups the values of the devices are not added up, they are averaged.
AGS - Bot Protection Tab
The AGS - Bot Protection tab shows the bot score distribution of the requests that come to the AGS-enabled vService. The three panels on the tab are in common with the Dashboard dashboard under the Bot/DDoS Protected vServices; the detail of the score classes and the detection factors is located on that page.
The data is produced even if the Bot/DDoS protection is off
While AGS is on in the vService, the bot score is calculated in every case. If the Bot/DDoS protection or the bot protection inside it is off, AGS produces the bot score with a default configuration that works in the monitoring mode with all the factors; if the bot protection is on, its configuration is used. The Bot Protection Outcomes panel on the Bot/DDoS dashboard is not located on this tab in any case; the action results are read from the Bot/DDoS dashboard.
Bot Score Distribution
It shows the distribution of the bot score given to every request in twenty buckets of five points each; the buckets are colored with the color of the class they belong to (Clean, Suspicious, Bot, Bad Bot). The panel opens in the bar, stacked line and heat map views. Its detail is located in the Bot Score Distribution explanation.
Bot Score Classes
It shows the distribution of the requests among the four bot score classes. In the pie view only Total is printed as the summary.
Bot Detection Factor Distribution
It shows which detection factor is triggered how often, that is, what produces the bot scores. The series are listed in descending order according to their totals. Its detail is located in the Bot Detection Factor Distribution explanation.
Scope and Limits
INFO
- The access to the dashboard and the panels require the Load Balancer authorization. In a user who has only the WAF authorization, the screen does not open. The AGS-Enabled vServices tab in the Left Monitor Panel requires the Load Balancer authorization as well.
- The layout settings are not separated per vService. The panel adding, moving, resizing, the templates and the toolbar preferences are stored in a single place per user; an editing made in one vService is seen in all the AGS vService dashboards. The panels bound to a condition are affected for this reason: a tab edited in a vService that has no authentication or CAPTCHA provider does not contain the provider panel in question in the vServices that have a provider either; the panel is brought back with Reset to Default. These settings are independent of the layout of the Load Balancer, WAF and Bot/DDoS dashboards.
- At most 32 panels per tab and at most 16 custom templates per user can be created. When the limit is reached, a warning is displayed.
- A version update can reset the stored layout. When the dashboard record form changes, the stored templates, the panel layout and the toolbar preferences return to the default.
- The open tab is written to the address line. The view tab selection is preserved within the same navigation; if the tab information is carried in the address line (a shared link), this information takes precedence over the remembered selection and that tab is opened. When it is passed to another AGS-enabled vService in the Left Monitor Panel, the open view tab is preserved.
- Reset and delete operations require confirmation. Each of the template reset, template delete and full dashboard reset operations shows a separate confirmation window.
- The data is read from the session store of the AGS engine. The data of the session, authentication, lockout, MFA, storage, audit and uptime panels is gathered from the session store of the engine; in the moments when the store cannot be accessed, an interruption occurs in these panels. AGS Request Distribution is read from the counters of the load balancer, and AGS Container Memory and AGS Container Memory % from the resource usage of the engine, so they continue to produce data independently.
- The fine resolution history is shorter in the bot panels. The AGS panels go back 14 days in the minute resolution; in the panels on the AGS - Bot Protection tab the same resolution is kept for only 1 day. This difference is taken into consideration in long term comparisons.
- In cluster setups the merging changes according to the panel. AGS Uptime and AGS Container Memory show a separate series for every device, AGS Container Memory % takes the average of the devices; in the other panels the device values are added up.
- Panel operations. The gear menu in the top right corner of each panel contains two operations: Edit (the panel's settings) and Remove (removing the panel from the dashboard). By dragging from the handle in the bottom right corner of the panel, the panel is resized; during dragging, the target size is shown with a ghost frame and a badge in the
1 × 0.5format. When the panel height drops below a full card, the title and summary strip are hidden; they are displayed again when hovered over.
