
Smarter by Design.Simpler for Business
ICMP & Reflection
What Is ICMP & Reflection?
ICMP & Reflection meets the traffic sent to the device by the hand of other systems. The band is on the L4 DDoS Management screen and its explanation note gives its scope in a single line: ICMP traffic and reflection (Smurf) attacks.
The subject of the band is the source of the traffic rather than the payload it carries. The packets the rules here deal with mostly look like the answer to a request: the answer of an echo query, a connection reset or a name resolution response. The attacker does not produce these packets himself; he has them sent to the target by deceiving other systems. For this reason the band brings three separate surfaces together:
| Box | What it looks at |
|---|---|
| ICMP | Whether the ICMP traffic will be allowed at all: the echo queries, the echo replies and the neighbor discovery packets of IPv6. |
| Smurf | The ICMP echo query rate per source and the rate of the connection reset packets that come to the device. |
| Reflection & Amplification | The responses that come unrequested from the eight UDP services used in amplification attacks. |
4
Rules
ICMP 1 · Smurf 2 · Reflection & Amplification 1
2
Able to Send to Quarantine
Only the two rate limits; the two on/off settings cannot send
3
Adjustable Limit
Three rules have a limit per second; the ICMP permission does not carry a value
2
Requiring the Promotion Permission
The two rules that use the enforcement levels require the Mode Promotion permission
4
Carrying a Learning Lock
All four carry a Learning Lock switch because they produce measurements
In Force
In an Untouched Table
The catalog defaults are written together with the table: Allow · Monitor · Monitor · Disabled
The band has no setting of its own
The band and the boxes carry no editing element: neither a mode selector nor a pencil icon is found. Every rule is adjusted with the pencil in its own row, in its own edit window.
The names of the boxes show their scopes narrower than they are
The name of none of the three boxes describes the rule inside it exactly:
The ICMP rule of the Smurf box does not look for a broadcast address; it is a general limit that measures the echo query rate per source. Sending to a broadcast address, which is the distinguishing mark of the classic Smurf attack, is not a matching criterion in any rule of the band.
The second rule of the same box looks at TCP packets; it has nothing to do with ICMP.
The Reflection & Amplification box meets the situation in which the device is the target: it limits the unrequested responses that come to the device from the amplification services. It does not prevent the device from being used as a reflector to attack others.
The ICMP & Reflection Band on L4 DDoS Management
The band is located right below the UDP band. In the header there are the name of the band, the number of rules it carries in parentheses and below it the explanation note; at the top right there are the mode distribution badges.
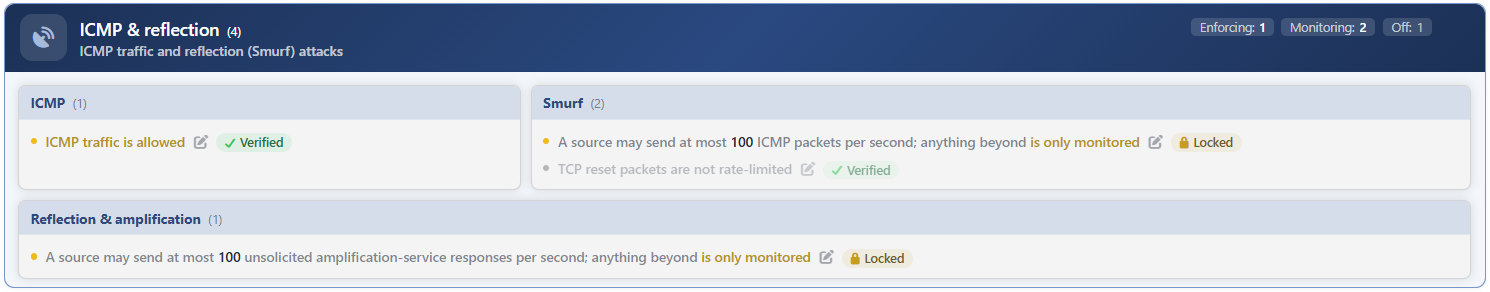 L4 DDoS Management - The ICMP & Reflection Band
| Element | Meaning |
|---|---|
| The title and the number | The name of the band and the number of rules in it: ICMP & Reflection (4). This number is fixed; the band carries the same four rules in every route table. |
| The explanation note | The fixed text that summarizes the scope of the band. |
| The distribution badges | The mode distribution of the four rules of the band: Enforcing, Monitoring and Off. A badge whose number is zero is not displayed. |
| The three boxes | In the header of every box there are its name and the number of rules it carries. |
The Enforcing number on the band and the number on the status card do not count the same set
The badges of the band count all four rules. The status card, on the other hand, takes into the jury only the rules that use the enforcement levels; in this band these are the ICMP Smurf: Pkt Limit and Reflected UDP rules.
When the ICMP permission is on, it is written into the Enforcing column of the band, but it does not enter any column of the card; the TCP reset limit is outside the card in the same manner. For this reason the badges of the band and the numbers of the card never overlap exactly in this band.
This is not an inconsistency but the two counters answering different questions: the band answers "how many rules are in force", and the card "how many rules can stop an attack".
Rule Modes
The four rules of the band use three separate value sets. This is the most distinctive feature that separates the band from the other protocol bands.
| Rule class | The values offered | How many rules |
|---|---|---|
| The ones that use the enforcement levels | Disabled · Monitor · Block · Quarantine | 2 |
| The permission setting | Allow · Deny | 1 |
| The on/off setting | Enabled · Disabled | 1 |
The color of the row is the color of the mode
At the beginning of every rule row there is a status dot and its color shows the mode of the rule:
| Mode | Dot |
|---|---|
| Block and Quarantine | Green |
| Monitor | Amber |
| Disabled | Dim gray |
| Enabled in an on/off setting | Green |
In the two rules that use the enforcement levels the action word inside the sentence is colored separately: amber in the monitoring mode, red in the enforcement mode. In the permission setting the whole of the sentence is highlighted, and in the on/off setting only the limit value.
The row of the permission setting is never green
The ICMP permission is not a protection but a permission: its being on passes the traffic, and its being off blocks it. For this reason the row is not displayed green in the Allow value either; the dot and the sentence (ICMP traffic is allowed) are displayed amber. In the Deny value, on the other hand, the row fades and the dot becomes dim gray, but the sentence (ICMP traffic is denied) is displayed red.
In the other three rules the color works as expected: enforcement green, monitoring amber, off gray.
The default value and the value the box is born with are not the same thing
In the rule catalog all four rules have a default value and these values are in force: the catalog defaults are written to the table while the route table is being created and in the configuration check at device startup, and in addition, in every network write the fields whose value remains undefined are filled again.
For this reason, in a route table that has never been touched, the band does not read Off 4. The ICMP permission is born Allow, the two rate limits Monitor and the TCP reset limit Disabled; the band reads Enforcing 1 · Monitoring 2 · Off 1.
The way to return all the rules to the catalog defaults at once is the returning to the default operation on the Learning strip.
Badges on the Row
At the right end of the rule row, where the sentence ends, there are small indicators. Their order from left to right is fixed: padlock → pencil → verdict badge.
| Indicator | What it is | When it is seen |
|---|---|---|
| Padlock | A lock icon without a word, on its own. It is the operator's Learning Lock switch. | While the learning lock of the rule is on. |
| Pencil | It opens the edit window of the rule. | While there is change authorization. |
| Verdict badge | A clickable badge carrying an icon and a word. It is the verdict of the learning engine about this rule in the last round. | If the engine has run at least one round. |
The verdict badge shows one of four words: Suggestion (there is a recommendation waiting to be applied), Locked (the engine has a change but it cannot be applied), Learning (there is no word to say yet) and Verified (the current setting was found in place).
In two rules of the band the badge never turns into a recommendation
The ICMP permission and the TCP reset limit carry a Learning Lock switch, but the learning engine never produces a recommendation for these two rules: since neither of them carries an enforcement level, there is no mode the engine could promote.
For this reason the padlock switch in these two rules protects nothing. Turning the switch on or off does not change the behavior of the rule.
Edit Window
The pencil that comes right after the sentence in every row opens the rule's own edit window. The title of the window is in the form Rule settings · <rule name>.
| Element | When it is found |
|---|---|
| The information band | In every rule. It shows the catalog definition of the rule. |
Status | In every rule. The option set changes according to the type of the rule: four levels, Allow · Deny or Enabled · Disabled. |
Learning Lock | In every rule. Since all four rules of the band produce measurements, the switch is found in all four. |
Limit per Second | In three rules. It is not found in the ICMP permission; that rule has no adjustable value. |
Save | In every rule. It is inactive while there is a validation error. |
The saving updates only the changed fields and takes effect immediately. If no field has changed, the request is not sent.
Rules in the Box
ICMP
Whether the ICMP traffic will be allowed; the results of turning the permission off other than the echo queries.
→
Smurf
The ICMP echo query rate per source and the general rate of the connection reset packets that come to the device.
→
Reflection & Amplification
The limit per source of the UDP responses that come unrequested from the eight amplification services.
→
Scope and Limits
INFO
- The band is displayed with the same four rules in every route table. The rules do not change according to the route table; only their modes and limits change.
- The band and the boxes have no editing element of their own. The editing is in the pencil of every row.
- Only two rules can send a source to quarantine; the ICMP permission and the TCP reset limit cannot send.
- In an untouched route table the catalog defaults are in force: the ICMP permission is born Allow, the two rate limits Monitor and the TCP reset limit Disabled.
- The two rate limits cover the traffic passed through the device as well. Since the rules are applied before the routing decision, they are not limited to the packets directed at the device.
- The TCP reset limit does not measure per source; it uses a common budget per IP version and is applied only to the packets that come to the device.
- The measurements do not separate the IP versions. The graph of a rule shows the IPv4 and IPv6 traffic together. The only exception is the counter of the ICMP permission; it counts only the IPv4 echo queries.
- The settings are per route table and are written to both devices in a cluster; the measurements and the quarantine lists, on the other hand, are per device.
- The sources in the exemption list are not caught by the two rate limits and are not written to the measurements of these two rules. The TCP reset limit, on the other hand, does not recognize the exemption list in this manner; the packets of the sources on the list are not passed through the rate budget of the rule and fall to the general rule at the end of the chain.
- The editing requires change authorization in the Network area. With a monitoring-only authorization the band and the sentences are displayed, the pencil icons are not displayed. While the network configuration is locked during synchronization, the editing is closed as well.
