
Smarter by Design.Simpler for Business
DNS Forwarder Profiles
What Is a DNS Forwarder Profile?
DNS Forwarder Profile is a reusable recursive resolver configuration that defines to which upper DNS servers a GTM DNS service will forward the queries outside its own zones: the default forwarding addresses (Forwarding Address), the optional domain-name-based rules (Domain Based Forwarding) and the optional raw configuration lines (Meta Data).
The profile does nothing on its own; it is assigned to a DNS service from the DNS Forwarder field in the Service Management form. When it is assigned, the service runs a separate resolver component in front of the authoritative DNS server and the queries coming to the front-end IP addresses of the service reach this resolver first: the own zones of the service, the domain name rules and the default addresses take place in a single forwarding table and the query goes to the entry that has the longest matching suffix with its name: the zones of the service to the authoritative server with an internal connection, the domain name rules to their own addresses and everything else to the default addresses. The front-end addresses marked DIRECT skip the resolver and go directly to the authoritative server.
Resolver
In front of the service
When it is assigned, the DNS service works with a recursive resolver component
A single table
Forwarding rule
The local zones, the domain name rules and the default addresses; the longest matching suffix wins
DIRECT
Skipping per address
On a front-end address basis the resolver is skipped and only the authoritative answer is given
IPv4 / IPv6
Address format
One address per line; an optional port
Service
Status and charts
The profile does not have a status; Forwarder error / absent and the Forwarder tab appear on the DNS service
Cluster
Per device
Every device runs its own resolver; the profiles are transferred to the peer device
How does it work?
- The profile is selected from the DNS Forwarder field of the DNS service; the service starts a resolver component in front of the authoritative server and routes all the front-end IP addresses that are not marked DIRECT to this component.
- For the name of the incoming query the longest matching suffix in the table is selected: if a zone of the service matches, the answer is taken from the authoritative server and is not forwarded to the upper servers.
- If a Domain Based Forwarding rule matches, the query is forwarded to the addresses of that rule, and if none of them matches, to the default addresses in the Forwarding Address list. The row order does not determine the priority; a rule that is more specific (with a longer suffix) than a zone of the service routes that subtree to the addresses of the rule instead of the authoritative server.
- The answer that returns from the upper server is transmitted to the client; the query rate, the bandwidth, the cache and the latency are monitored on the Forwarder tab of the DNS service dashboard.
The access and the verification
A client restriction cannot be defined on the resolver; the clients that can reach the front-end IP address receive an answer. For this reason the front-end addresses of the services that have a forwarder assigned must be accessible only from the targeted networks. The resolver transmits the DNSSEC records coming from the upper servers but does not verify them.
When Is It Used?
- When all the DNS queries of the clients must be met over TR7 and the names for which TR7 is not authoritative must be forwarded to the upper servers,
- When it is desired that the internal network domain names (e.g.
corp.local) go to the corporate DNS server and the other queries to the public resolvers, - When some front-end addresses in the same service must give only an authoritative answer (DIRECT) and the others must perform recursive resolution.
Operational Best Practices
- More than one forwarding address must be defined. When there is a single server in the Forwarding Address list, the failure of that server stops all the resolution outside the scope.
- The internal network zones must be separated with a domain name rule. The corporate zones are routed to the corporate DNS server with Domain Based Forwarding and the remaining queries to the default addresses; since the rules are applied with the longest suffix matching, the more specific domain name always wins; a rule written under the own zone of the service takes that subtree away from the authoritative server.
- DIRECT must be used on the externally open front-end addresses. Since the resolver does not make a client restriction, the front-end addresses that face the internet must be marked DIRECT and limited to giving only an authoritative answer; the recursive resolution must be left on the addresses that face the internal network.
- The profile changes must be made in a maintenance window. Every save that changes the addresses, the rules or the meta data restarts the resolver component of the services that use the profile; there is a short interruption on the front-end addresses that are not DIRECT. Changing only the name does not affect the running component.
- The meta data must be used only when necessary. The entered lines are written into the resolver configuration as they are and are not checked; an entry that collides with the automatically produced configuration keys can break the local zone resolution.
- The references must be reviewed before deleting. The deletion turns off the recursive resolution on the services that use the profile without a warning; the service form shows the Select an option error in that field.
How to Add?
A new DNS Forwarder Profiles profile is added through the TR7 web management interface with the steps below:
- The Configuration Menu is opened by clicking the TR7 logo at the bottom left.
- The GTM → DNS Forwarder Profiles → Add steps are followed.
- A unique and descriptive name is entered for the profile.
- One upper DNS server is written per line into the Forwarding Address list; if necessary, the Domain Based Forwarding rules and the Meta Data lines are added.
- The profile is added by clicking the
Addbutton.
TIP
Reaching the page via quick search
Instead of navigating the menu step by step, the related page is reached directly by using the search bar in the bottom left corner of the screen. The search bar opens with the Alt + T shortcut on Windows and Opt + T on macOS; typing the name of the feature being searched for is then sufficient.
The created profile can be used on one or more DNS services.
DNS Forwarder Profiles Listing Screen
By following the GTM → DNS Forwarder Profiles path, the list of all the DNS forwarder profiles added on the TR7 device is reached. Profile adding, editing and deleting operations are performed through this screen.
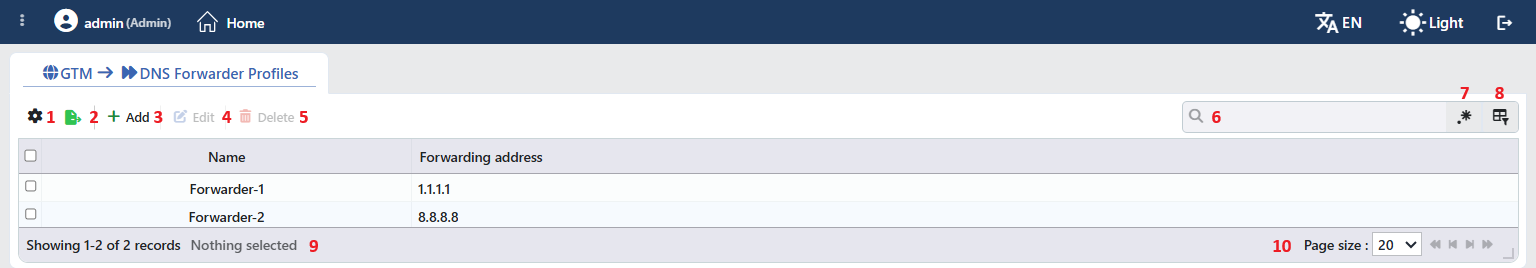 DNS Forwarder Profiles Listing Form
The table opens with the following columns by default:
| Column | Description |
|---|---|
| Name | The name of the profile. |
| Forwarding Address | The default forwarding addresses, comma separated. The domain-name-based rules do not appear in this table; they are listed in the preview and in the form. |
There is no column hidden by default; these two columns are in the column selector. The table is not sorted by default (the profiles are listed in the order in which they were added); when a column header is clicked, descending sorting is applied first, then ascending, and on the third click the sorting is removed. The profiles do not have a working status; there is no status column or status circle on this screen.
The items in the toolbar are arranged from left to right in the following order; the last two items (Page Information and Page Size) are in the information strip under the table. There is no filter card and no Usage Filter on this screen.
Columns
Which columns are shown in the table is selected; both columns are on by default. In the same panel, columns are reordered by dragging and alignment is selected per column; the row height is fitted to the page with the Fit rows to the page button, and the column layout is reset to default with the Reset button. When the width badge next to a manually widened column is clicked, the column returns to the automatic width. The layout is stored per user.
Export
The table is exported as Excel, CSV or PDF by clicking the Export button. In the window that opens, the Filename, Format and Data Source, together with the Columns to be exported, are determined; the remaining fields are displayed according to the format: CSV Separator for CSV, Excel Sheet Name for Excel, and Page Orientation and Page Size for PDF.
Add
By clicking the Add button, the form for creating a new profile opens in the Add tab.
Edit
By clicking the Edit button, the editing form of the selected profile opens in the Edit tab. The button becomes enabled only when a single profile is selected. The editing form is the same as the add form; all the fields can be changed and the change is saved without asking for confirmation.
WARNING
A save that changes the addresses, the rules or the meta data restarts the resolver component of every DNS service that uses the profile; during the restart the queries coming to the front-end addresses of that service that are not DIRECT remain unanswered. The authoritative server is not affected; changing only the name does not require a restart.
Delete
When one or more profiles are selected and the Delete button is clicked, the related profiles are deleted. Before deleting, the "Are you sure?" confirmation is asked. The button is passive while there is no selection.
WARNING
A profile that is in use can also be deleted and the confirmation window does not show in which services the profile is used; before deleting, the Used in tab on the preview panel must be checked.
The resolver component of the services that use the deleted profile is removed and all their front-end addresses are routed directly to the authoritative server; the queries outside the own zones of the service are no longer resolved and, since the status of the service appears as OK, the loss is not understood from the status. In the service form the DNS Forwarder switch stays on and the field gives the Select an option error until a new profile is selected; the Forwarder tab on the service dashboard continues to be visible but the four charts on the tab are not created at all because the profile cannot be found. The deletion operation is written into the user operation record.
Search
Used to search all information in the table.
RegExp Search
Used to search all information in the table with a regular expression (RegExp).
Column Based Search
Used to perform a column-based search on the information in the table; a separate search line opens for every column and next to every box there are the Negate button that reverses the result and its own RegExp switch.
Page Information
Contains information about the total number of defined profiles and the number of profiles displayed in the list: Showing N-M of T records and the number of selected profiles (N selected, or Nothing selected when there is no selection).
Page Size
The maximum number of profiles to be displayed on the page is selected. The default is 20; the options are 5, 10, 20, 50, 100, 200, 500 and All. With the arrow icons next to it, the pages are switched between.
Right-Click Menu
When a row is right-clicked, a menu with the profile's name in its title opens. Both operations in the menu apply only to the right-clicked profile; a selection made in the list does not affect the menu.
| Operation | What it does |
|---|---|
| Edit | Opens the editing form of the profile in the Edit tab; it is the same as the form opened by the Edit button in the toolbar. |
| Delete | Deletes the right-clicked profile; the same confirmation question as the deletion in the toolbar is displayed. |
Preview of the Selected Profile
When a row in the list is clicked, the preview of the profile opens on the right of the screen; when the selected row is clicked again, the panel closes. In the title there are the name of the profile and the DNS Forwarder Profile subtitle, and at the top right there are two operations; a status circle does not take place.
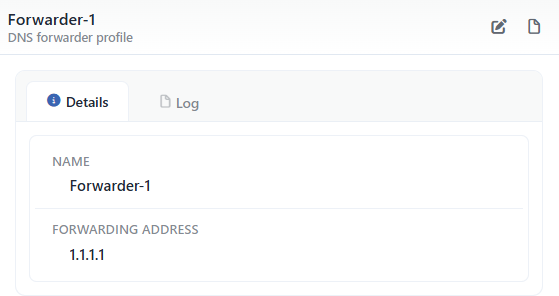 Preview of the Selected Profile
| Operation | What it does |
|---|---|
| Edit | Opens the editing form of the profile in the Edit tab. The same form is also opened with the Edit button in the toolbar and with Edit in the right-click menu of the row. |
| Log | Opens the user operations (adding, editing, deleting) that belong to the profile in a window, without leaving the page. |
The panel has three tabs; the last one is displayed only if there is a DNS service that uses the profile:
Details
Lists the configuration lines of the profile (the table below).
Log
Lists the user operations performed on the profile as a timeline.
Used in
Lists the DNS services that select the profile from the DNS forwarder field; the badge next to the tab name shows the number of usages. When a row is clicked, it is passed to the related service.
The rows in the Details tab are as follows, in order:
| Row | Description | Visibility condition |
|---|---|---|
| Name | The name of the profile. | Always |
| Forwarding Address | The default forwarding addresses, comma separated. | Always |
| Domain Based Forwarding | Every rule in one line in the domain name -> address, address form. | If a rule is defined |
The meta data are not listed in the preview. The same lines are also shown under the DNS Forwarder row in the preview of the DNS service that uses the profile; in the profile selector in the service form, the eye icon next to every option opens this preview in a small window and the pencil icon opens the editing form of the profile in a window.
Profile Add Form
A new DNS forwarder profile is added on the TR7 device by following the GTM → DNS Forwarder Profiles → Add steps.
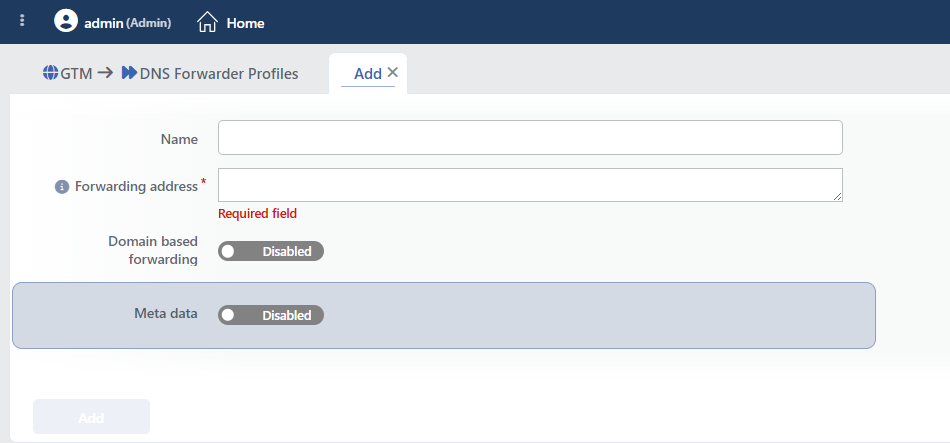 DNS Forwarder Profile Add Form
INFO
Name
The name of the profile is entered. The name identifies the profile in the list, in the profile selector in the DNS service form and in the user operation record. The name can be left empty and the same name can be used in more than one profile; a profile whose name is empty appears with an empty line in the list and in the preview, and with its identifier in the preview title and in the selector of the service form. A distinctive name must be given.
INFO
Forwarding Address Required
The upper DNS servers to which the queries that are outside the own zones of the service and that do not match any domain name rule will be forwarded are entered; one address is written per line. While the field is in focus, the Each forwarding address (IPv4/IPv6/IPv4:port/IPv6:port) can be written as a new line information appears.
| Format | Example |
|---|---|
| IPv4 | 8.8.8.8 |
| IPv4:port | 8.8.8.8:5353 |
| IPv6 | 2001:db8::1 |
| [IPv6]:port | [2001:db8::1]:5353 |
Every line must comply with one of these formats; when the field is left empty, the Required field error and when an invalid line is entered, the Correct invalid inputs error is given and the save is prevented. A domain name is not accepted; an IPv6 address with square brackets is written only together with a port ([2001:db8::1]:5353).
INFO
Domain Based Forwarding Default: Disabled
It is opened with the switch; different upper servers are defined for certain domain names. When the switch is turned on, the list comes with one empty row and the form cannot be saved until its two boxes are filled; new rules are added with the Add button with the plus icon under the list. While there is a single row in the list, the row deleting and sorting handles are not displayed, and they appear from the second row on.
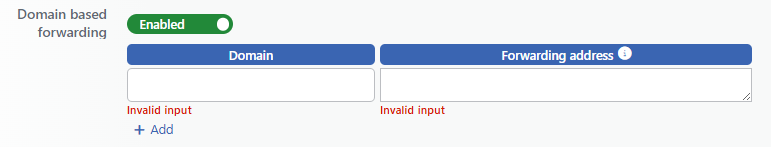 Domain Based Forwarding
Domain
The domain name to which the rule will be applied (e.g. corp.local); the subdomains are covered as well and a name with a wildcard character (*.corp.local) is accepted. A single-label name (local) and an invalid domain name give the Invalid input error in the row.
Forwarding Address
The upper servers to be used for this domain name; the format and the line rules are the same as the default Forwarding Address and at least one address must be entered. An invalid line gives the Invalid input error in the row of the rule. The address format information is displayed in the tooltip of the ⓘ icon in the column header.
The query is routed to the rule that matches with the longest suffix among the defined rules; if no rule matches, it goes to the default addresses. The own zones of the service also take place in the same table: a rule that is more specific than the zone name routes that subtree to the addresses of the rule instead of the authoritative server.
INFO
Meta Data Default: Disabled
It is opened with the switch; the key=value lines to be written directly into the resolver configuration are entered. In every row there are two boxes without a header; while they are empty, the Variable name and Value hint texts appear (the value can be left empty). A row is added with the Add button with the plus icon under the list. The entries are not checked and are written as they are; a row whose key is left empty is skipped without a warning. Since the lines are put at the beginning of the configuration, an entry that carries the same name as an automatically produced key takes the place of that key. The field is for the advanced settings that cannot be met with the standard fields (e.g. the cache directives).
INFO
Add
The profile adding process is completed by clicking the Add button. While there is an erroneous field in the form, the button is passive; the adding does not ask for confirmation and when the record is completed, the Add tab closes.
Operating Mechanism
INFO
- The forwarding table. For a service to which a profile is assigned, the resolver works with a single table: every zone of the service to the authoritative server (an internal connection), every Domain Based Forwarding rule to its own addresses and everything else (
.) to the Forwarding Address list. The matching is made with the longest DNS suffix; the row order does not determine the priority and a rule that is more specific than a zone of the service wins that subtree. - The client address. The address of the client that makes the query is transmitted only to the authoritative server so that the geographic record selection continues to work; it is not transmitted to the upper servers.
- The cache. The resolver uses its own cache with the default settings; there is no cache setting in the standard fields of the profile, and if it is necessary, a directive is written with the Meta Data. The cache settings on the DNS service affect only the authoritative server.
- The resources. The QOS settings of the service (the cores, the processor priority and limit, the memory limit) are applied to the resolver component in the same way.
- The status and the restart. The profile does not have a status. If the resolver is not working while the authoritative server is working, the service status becomes Forwarder error, and if the component is not present at all, Forwarder absent; if the authoritative server is not working, only Error / Absent appears. The Restart Service operation in the service preview restarts the resolver together with the authoritative server.
- The monitoring. On the Forwarder tab of the DNS service dashboard there are the Forwarder Query Rate, Forwarder Bandwidth, Forwarder Cache and Forwarder Latency charts; there is no chart for the profile itself.
- The cluster. The profiles are transferred to the peer device together with the GTM configuration; every device runs its own resolver independently, there is no primary device distinction.
Scope and Limits
INFO
- The screen requires a GTM license and full GTM authorization. The GTM tab is visible with the display authorization; this screen opens only on the users who have full authorization in the GTM area, and if there is no GTM module in the license, the Not covered by your license card is displayed.
- There is no status and no filter. There is no status column, status circle or filter card in the list; the search box is used.
- There is no client restriction and no DNSSEC verification. A client restriction cannot be defined on the resolver and the DNSSEC verification is off.
- There is no connection test. In the form there is no button that tests whether the upper server answers or not.
- The name is not required and not unique. The profiles without a name or with the same name can be saved.
- The deletion does not clean the dependencies. The services that use the profile lose the recursive resolution; the service form must be updated manually.
- The logs. The user operations are monitored in the Log window on the preview panel and on the GTM Logs screen; the working logs of the resolver are not listed on this screen.
Usage Location
The profile is assigned from the DNS service form on the Service Management screen:
1
Step 1 The service form
The service is selected in the GTM → GTM Services → Service Management path and the editing form is opened with Edit (or a new service is added).
2
Step 2 The profile selection
The Enabled / Disabled switch of the DNS Forwarder field is turned on and the profile is selected from the list; the moment the switch is turned on, the field gives the Select an option error until a profile is selected and the form cannot be saved. With the Add button of the selector, a new profile can be defined and assigned in the same window.
3
Step 3 The DIRECT mark
When the switch is turned on, the DIRECT box appears in every row in the Frontend IP table. The queries coming to the marked front-end address skip the resolver and go directly to the authoritative server; only the own zones of the service are answered.
4
Step 4 The save
When the service is saved, the resolver component is started and the front-end addresses that are not DIRECT are routed to it. If the resolver is not working while the authoritative server is working, the status of the service appears as Forwarder error, and if the component has not been created at all, as Forwarder absent.
