
Smarter by Design.Simpler for Business
TCP Logs
What Are TCP Logs?
TCP Logs are the connection-level access log that keeps every TCP connection passing through an L7 TCP vService as a single record. Unlike HTTP Logs, they work not at the request/response level but at the connection level: each record represents one client connection and contains the client address, the listening address of the vService and (if TLS is terminated) the TLS version and cipher suite information.
TCP Logs are the basic way to monitor traffic for services that do not carry HTTP semantics (method, host, path, status code), such as databases, e-mail (SMTP) and custom TCP protocols. At a glance, it is seen "where a connection came from, which listener it landed on and how it was encrypted". Which Backend Service the connection was distributed to is not kept in this record; the record is stamped before the distribution decision is made. vService Sessions is used for this information.
Connection Log
Per-connection log
Each TCP connection in a single record
Connection
Client → vService
Client and vService listening addresses
Visibility
Connection insight
Who connected where, and when
TLS
Encryption information
TLS version and cipher suite
Protocol Independent
Any TCP service
For non-HTTP TCP applications
Load Balancer
Part of the product
Enabled separately for every vService
HTTP Logs are used for services that carry HTTP semantics, and TCP Logs for non-HTTP TCP-based services. TCP Logs are a part of the Load Balancer module and are enabled separately for every vService.
Supported vService Types
HTTP
L7 TCP
Network
How Are TCP Logs Enabled?
TCP Logs start being produced when a Log Profile is assigned to the L7 TCP vService. The Log profile is enabled from the LOG field in the Details panel of the vService form, and a profile is selected. It is off by default; when it is enabled, the default (Default) Log profile comes selected.
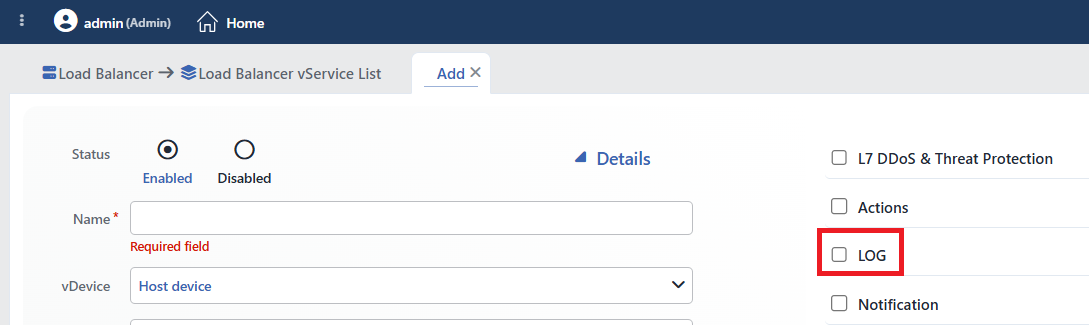 How Are TCP Logs Enabled?
Default Log Profile
When the Default Log profile is assigned, no sending to external log systems (syslog / SIEM) takes place; only TCP Logs are enabled for the related vService. The records are kept on TR7 and are viewed from the Logs & Tracking tab. For external forwarding, target Log addresses must be defined in the Log profile.
1
Step 1 The vService edit form is opened
The edit form of the related L7 TCP vService is opened by following the Load Balancer → Load Balancer vService List path.
2
Step 2 LOG is enabled from the Details panel
The Details panel is opened in the vService form, the LOG field is enabled and the Log profile to be applied is selected.
3
Step 3 The change is saved
When the form is saved, a TCP Log is created for each TCP connection passing through the vService.
Log Profile and External Forwarding
The Log profile configures not only the keeping of records but also their forwarding to external log servers (syslog): the target Log addresses (IP:Port), the Log standard (RFC 3164 / RFC 5424, etc.), the line format and the sampling settings are defined in the Log profile. Details are located on the Logs page.
Viewing TCP Logs
- Left Monitor Panel is opened.
- Load Balancer vServices is selected from the category tabs at the top left.
- The vServices defined on TR7 are listed.
- The vService to be monitored is clicked; the screen opens with the Dashboard tab that carries the vService's name.
- On the screen that opens, the Logs & Tracking tab is clicked and TCP Logs is selected.
TCP Logs Listing Screen
When the TCP Logs source is selected in the Logs & Tracking tab, the records are listed as a table. When the screen opens, the records are fetched automatically if the vService is in the enabled state; when the log source is changed, the fetch is renewed. Filter selections are applied to the fetched records and do not start a new fetch.
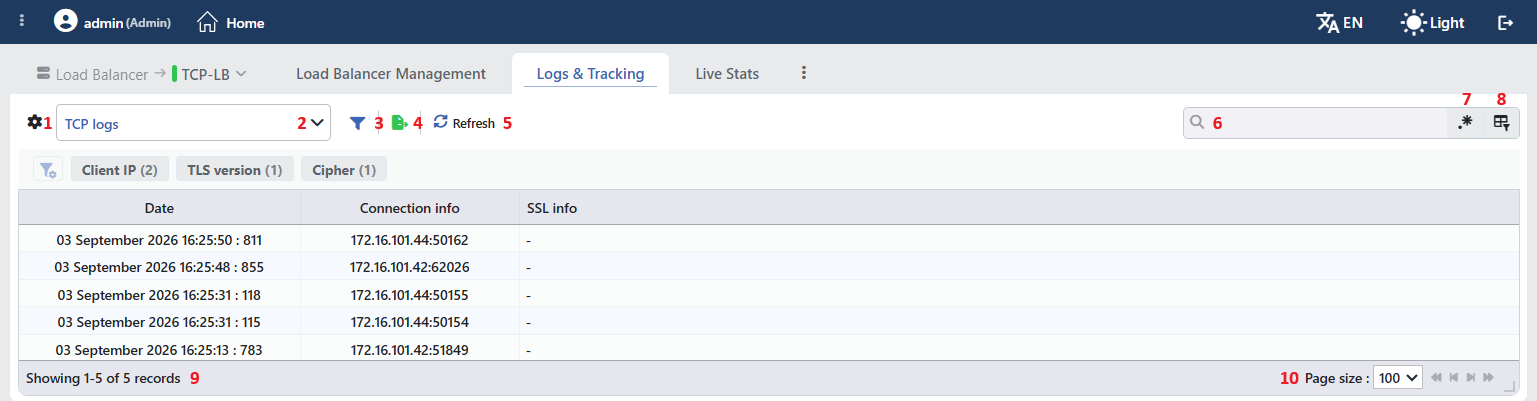 TCP Logs Listing Screen
The table opens with only three columns by default:
| Column | Description |
|---|---|
| Date | The date and time the connection was recorded (with millisecond precision). |
| Connection Info | The address information of the client that established the connection (client IP and port). |
| SSL Info | The cipher suite and TLS version of the connection, written in this order on a single line. If the vService does not terminate TLS (passthrough), - is shown. |
The Source column is hidden by default and is added from the column selector; it shows the name of the device that produced the record and is meaningful only in cluster setups.
The items in the toolbar are arranged from left to right in the following order; the last two items (Page Information and Page Size) are located in the information strip below the table.
Columns
Which columns are shown in the table is selected. In the same panel, columns are reordered by dragging and alignment is selected per column; the row height is fitted to the page with the Fit rows to the page button, and the column layout is reset to default with the Reset button. The layout is stored per user.
Logs Type
Determines the log source to be listed. TCP Logs is selected to view TCP Logs. The selector is populated according to the vService's configuration and leaves out the WAF and Bot/DDoS sources.
Filter
Opens and closes the filter panel; the panel comes open by default. While the panel is open, the filters are listed above the table as a strip of cards, and the number next to a card shows how many distinct values that filter carries in the fetched records. When a card is clicked, the values of that filter open as chips; the number next to each chip is the number of records carrying that value, and when a chip is selected, the table is narrowed to that value.
Only three filters are defined for TCP Logs, and all three are open by default:
| Filter | Description |
|---|---|
| Client IP | The IP address of the client that established the connection. |
| TLS Version | The TLS version of the connection (TLS 1.2, TLS 1.3, etc.). Connections where TLS is not terminated are grouped as Plain HTTP. |
| Cipher | The cipher suite of the connection. |
Export
The table is exported as Excel, CSV or PDF by clicking the Export button. In the window that opens, the Filename, Format and Data Source, together with the Columns to be exported, are determined; the remaining fields are displayed according to the format: CSV Separator for CSV, Excel Sheet Name for Excel, and Page Orientation and Page Size for PDF.
Refresh
The records are fetched again by clicking the Refresh button. Since filter selections work only on the fetched records, this button is the way to get up-to-date records from the server. While fetching is in progress, the button stays inactive and shows a spinning icon. If the vService is stopped, the button stays inactive; since TCP records are read from a live table, records cannot be fetched from a stopped vService.
Search
Used to search all information in the table.
RegExp Search
Used to search all information in the table with a regular expression (RegExp).
Column Based Search
Used to perform a column-based search on the information in the table.
Page Information
Contains information about the total number of fetched records and the range of records displayed in the list: Showing N-M of T records. Since rows cannot be selected in this source, the number of selected rows is not shown.
Page Size
The maximum number of records to be displayed on the page is selected. The default is 100; the options are 50, 100, 250 and All. The selection is not stored.
Record cap
TCP records are written not to a file but to a live table. The table keeps at most 1,000 connection records, and a record expires after 24 hours; when the cap is exceeded, the oldest records give way to new ones. This is also what the absence of the Line Limit box in the toolbar means in practice.
Line Limit is not present in this source
The Line Limit box, which limits the number of records to be scanned, is displayed only in file-based sources (HTTP Logs, Debug Logs and WAF logs); it is not present in the TCP Logs toolbar.
Preview of the Selected Log
When any record in the list is clicked, a preview panel of that connection opens on the right side of the screen. Unlike HTTP and Debug Logs, this panel is tabless: there is no Summary, Request and Response separation, because the TCP record does not carry request- and response-level data. The fields that are meaningful at the connection level are shown one below the other.
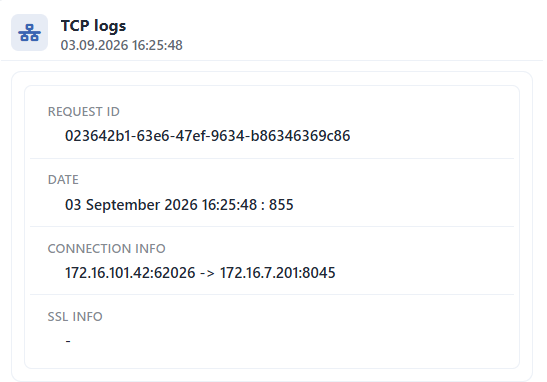 Preview of the Selected TCP Log
Information in the preview panel:
| Information | Description |
|---|---|
| Request ID | The unique identifier assigned to the connection. If the record has no identifier, the row is not displayed at all. |
| Date | The date and time the connection was recorded (with millisecond information). |
| Connection Info | The address chain of the connection. The chain has two nodes; since the record is stamped before the Backend Service is selected, there is no third node. CLIENT IP:Port→TR7 vService IP:Port |
| SSL Info | The cipher suite and TLS version of the connection are written on a single line in the <cipher suite>, <version> format. A labeled sub-table like the ones in HTTP and Debug Logs is not displayed. If the vService does not terminate TLS (passthrough), this field comes as -. |
