
Smarter by Design.Simpler for Business
AGS-Enabled vService List
What Is the AGS-Enabled vService List?
AGS-Enabled vService List is the management page on which all the vServices that have the AGS access control enabled on the device are listed on a single screen. On each row the running state of the vService, its name, the addresses it listens on, the operating mode of the access service and the number of nodes in the flow are displayed.
The screen is at the same time the place where AGS is turned on and off in bulk: the access control is started or removed by selecting one or more HTTP vServices. A default access service is created automatically for the vService on which AGS is turned on; the flow and the settings are edited from the AGS-Enabled vServices screens.
The L7 TCP and Network (Layer 4) vServices are not within the scope of AGS
Only the vServices of the HTTP type that have AGS on are in the list. The vServices of the L7 TCP and Network types are not displayed in this list; the list of the vServices on which the access control can be started is limited to the HTTP type in the same way.
How to Access?
The AGS-enabled vService list is reached through the TR7 web management interface with the following steps:
- The Configuration Menu is opened by clicking the TR7 logo at the bottom left.
- The AGS → AGS-Enabled vService List steps are followed.
- All the vServices that have AGS enabled on the device are listed.
TIP
Reaching the page via quick search
Instead of navigating the menu step by step, the related page is reached directly by using the search bar in the bottom left corner of the screen. The search bar opens with the Alt + T shortcut on Windows and Opt + T on macOS; typing the name of the feature being searched for is then sufficient.
vService Listing Screen
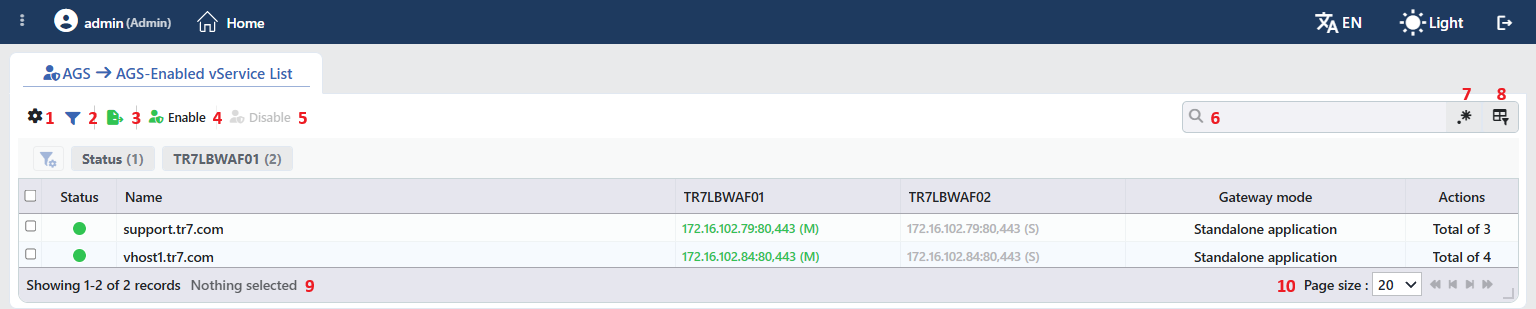
The list of all the vServices that have AGS enabled on the TR7 device is reached by following the AGS → AGS-Enabled vService List path. Starting and removing the access control on the vServices is performed on this screen.
 vService Listing Screen
The table opens with the following columns by default:
| Column | Description |
|---|---|
| Status | The instantaneous state of the vService is shown with a colored circle; the meaning of the colors is on the vService page. In a cluster configuration the circle is separated into one dot per device. |
| Name | The name of the vService. |
| IP | The addresses and the ports the vService listens on (e.g. 172.16.102.79:80,443). In a cluster configuration the addresses are shown in two separate columns and the header of each column carries the name of the related device (Server Name / Hostname); on the VIP addresses the (M) Master and (S) Slave labels are displayed and the cell color is given according to the state of the address on that device (Interfaces List › Interface and IP States). |
| Gateway Mode | The operating mode of the access service: Standalone Application, Portal or Portal Application. |
| Actions | The number of nodes in the access flow; the Allow and Deny end steps are included in the number as well (in the Total of N form). On a newly turned on vService the value is Total of 3. |
The column and filter layout (the visibility, the order, the width and the alignment) is stored on a user basis and is preserved in the following sessions. This layout is common to all the vService lists: a column hidden here comes hidden in the Load Balancer vService list of the same user as well.
The items in the toolbar are arranged from left to right in the following order; the last two items (Page Information and Page Size) are located in the information strip below the table.
Columns
Which columns are shown in the table is selected from the Columns window that opens by clicking the gear icon in the toolbar. In the same panel the columns are reordered by dragging and the alignment is selected per column.
Filter
The Filter button is used to filter the vServices shown in the list according to certain criteria. Two filter cards are offered in this list: Status and the filter of the address column; in a cluster configuration the address card carries the name of the device in its header. On each card the options are listed together with the number of rows that have that value; the selections on different cards are applied together.
The filtering view is customized: which filters are shown is selected, the order of the filters is changed and the view is arranged according to the need.
The active filters are displayed as labels below the toolbar; each filter is removed one by one with the close icon next to its label. The total effect of the filtering is written in the information strip below the table, as the number of shown and total rows.
Export
The table is exported as Excel, CSV or PDF by clicking the Export Table button. In the window that opens, Filename, Format, Data Source and the Columns to be exported are determined; the remaining fields are displayed according to the format: CSV Separator in CSV, Excel Sheet Name in Excel, Page Orientation and Page Size in PDF.
Enable
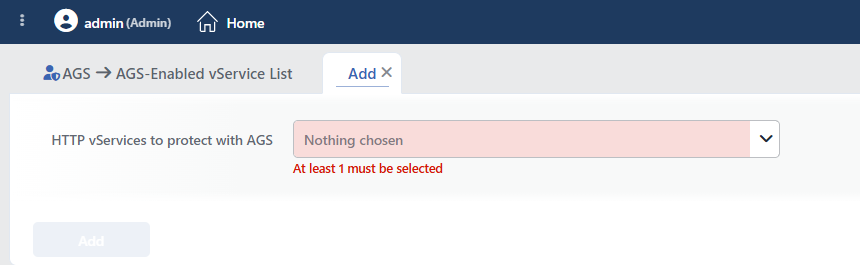
When the Enable button is clicked, a new tab headed Add opens next to the list.
 Enable
The HTTP vServices on which the access control is to be started are selected in multiples from the HTTP vServices to Protect with AGS field and are confirmed with the Add button. AGS is turned on on the selected vServices and their rows start to appear in the list.
When no selection is made, the field writes Nothing chosen; when the tab is opened while the selection is empty, the At least 1 must be selected warning is displayed under the field and the Add button is inactive until a selection is made. The tab is closed with the close icon in its header.
The access service of a newly turned on vService is created with the default settings: the flow starts with the built-in Basic Login form, the session protection policy is Standard Session Protection, the default lockout policies are Default Username Lockout and Default IP Lockout, the bot policies are Standard Rate Limiting, Bot Score CAPTCHA Challenge and Bot Score Deny, the page template is Default Page Template and the dictionary is Default Dictionary.
The default flow contains no authentication step
The flow of a newly turned on vService starts only with the Basic Login form; there is no Authentication Providers step in the flow. An authentication step must be added to the flow before the Backend Service is put into production.
Disable
When one or more vServices are selected and the Disable button is clicked, AGS is turned off on the related vServices and the rows are removed from the list. The button is inactive when no selection is made in the list.
The selection here is the selection made with the checkboxes at the beginning of the rows; clicking a row and opening its preview does not enable the button. The bulk selection box in the column header, on the other hand, selects all the rows that are filtered at that moment, including the ones on the other pages.
WARNING
The Disable operation shows no confirmation window; at the moment it is clicked the access control is removed on all the selected vServices and the users start to reach the Backend Service without verification. For this reason the selection must be verified before the button is clicked.
When AGS is turned off, the access service configuration of the vService (the flow, the policies, the template and dictionary selections) is not deleted; it is kept as long as the vService exists and the same configuration applies when AGS is turned on again.
The Enable and Disable operations are not merely a flag change: the configuration of the related vService is produced and applied again and the access engine is started or stopped accordingly. In a cluster installation, if the automatic synchronization is on, the change is propagated to the peer device as well. There is no upper limit for the number of selected vServices; the operation is applied in one go.
Search
Used to search the information in the table. The search works on the values that appear on the screen and without case sensitivity. The Status column is not included in the search; filtering by the state information is done from the Filter window.
RegExp Search
Used to search all information in the table with a regular expression (RegExp).
Column Based Search
Used to perform a column-based search on the information in the table.
Page Information
Information about the number of vServices displayed in the list is located here: Showing N-M of T records and the number of selected rows (N selected, and Nothing selected when there is no selection). While a search or a filter is active, the number here shows not the total number of vServices with AGS enabled but the number of rows that remain after the filtering.
Page Size
The maximum number of vServices to be displayed on the page is selected. On this screen the default is 20.
Right-Click Menu
When a row is right-clicked, a menu with two operations that has the name of the vService in its header opens. The operations are applied only to the right-clicked vService; a selection made in the list does not affect the menu.
| Operation | What it does |
|---|---|
| Edit | Opens the AGS Management tab of the vService; it is the same as the Edit icon in the preview header. |
| Remove AGS Access | Removes the AGS access control of the vService; like Disable in the toolbar, it does not ask for confirmation. It does not touch the vService itself and the access service configuration. |
The Delete, Enable, Disable and Reload operations in the Load Balancer vService list are not in this menu.
Preview of the Selected vService
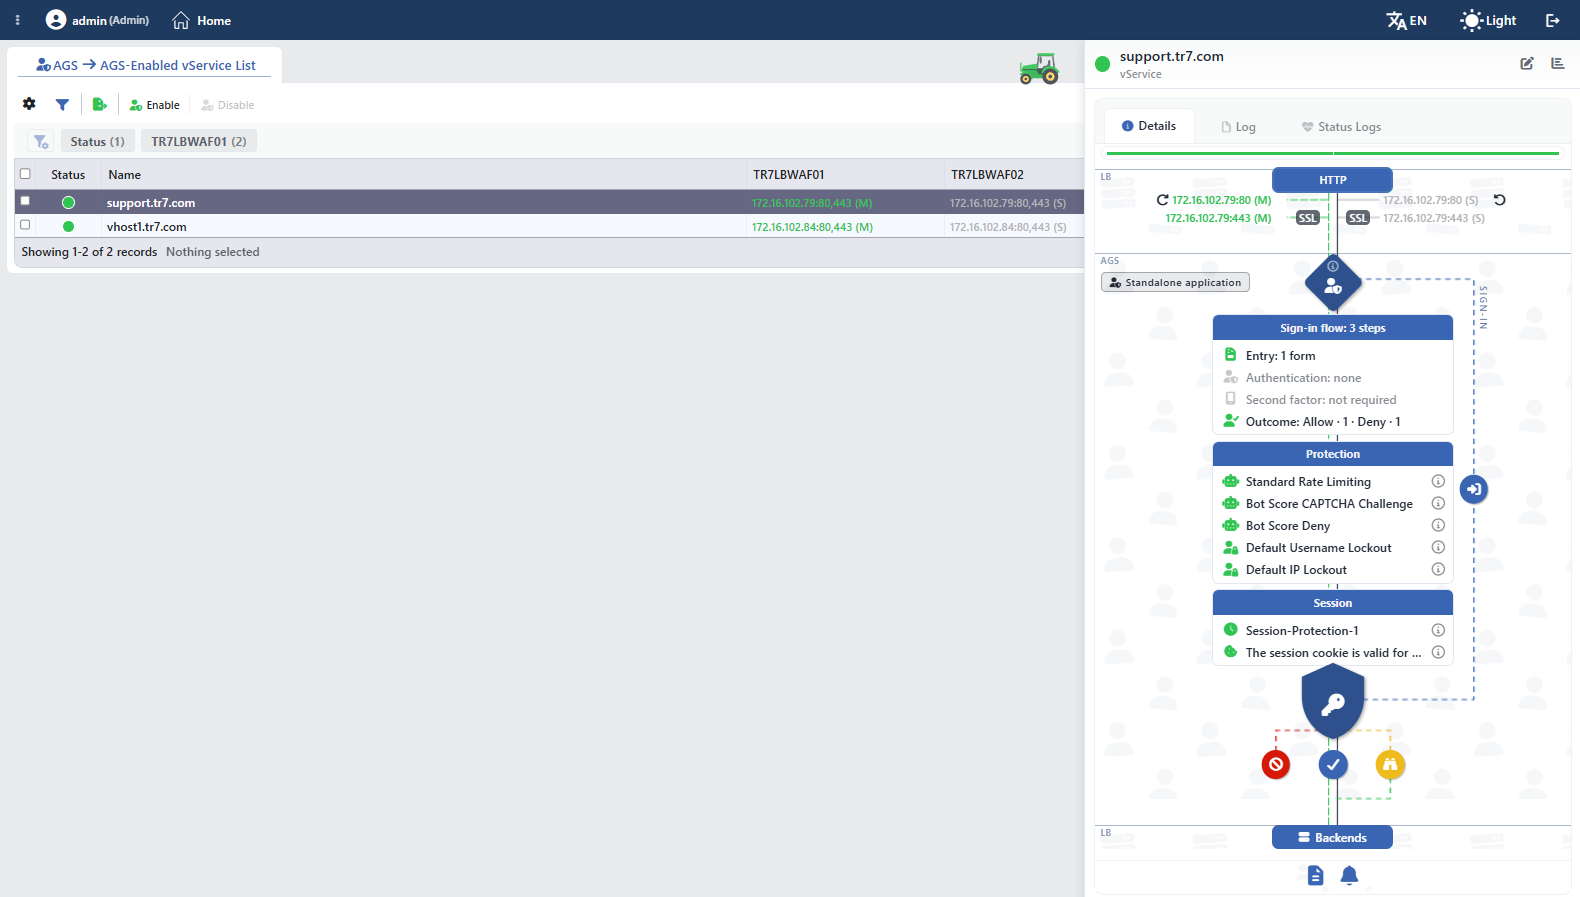
When a row in the list is clicked, the preview of the vService opens on the right of the screen; when the row is clicked again, the selection is removed. The header contains the status color of the vService, its name and the vService subtitle, and two operations are at the top right. Clicking a row alone does not move to another screen.
 Preview of the Selected vService
| Operation | What it does |
|---|---|
| Edit | Opens the AGS Management tab of the vService; the access service settings are edited group by group here. It is not displayed for a user who has read-only permission. |
| Dashboard | Opens the AGS Dashboard screen of the vService. |
Deleting, stopping, starting and reloading the vService are not in this preview.
There are three tabs in the panel:
Details
Shows the AGS configuration of the vService as a diagram on the path the request follows.
Log
Lists the history of the operations performed on the vService; the AGS turning on and off operations performed from the list screen are not written into this history.
Status Logs
Lists the state transition history of the vService (on which date it moved to which state).
The Details Diagram
The diagram consists of three bands and summarizes the path from the entry point of the request to the Backend Service.
| Band | Its content |
|---|---|
| The LB at the top | The entry point of the vService: the HTTP header, the addresses and the ports that are listened on. On the addresses that terminate TLS the SSL badge and in a cluster configuration the (M) and (S) labels are displayed. |
| AGS | The configuration of the access service. At the top left there is the operating mode badge (Standalone Application, Portal or Portal Application) and on the right edge the SIGN-IN label that marks the login path; the cards below are lined up in the middle. |
| The LB at the bottom | The Backends box the request reaches after the verification. |
The cards in the AGS band are as follows, in order:
| Card | Its rows |
|---|---|
| Sign-in flow: N steps | Entry gives the element that starts the flow (e.g. 1 form), Authentication the authentication steps (none if there is no step), Second Factor the MFA step (not required if there is no step) and Outcome the number of the end steps (e.g. Allow · 1 · Deny · 1). The number in the header is the number of steps in the flow. |
| Protection | The Bot Protection Policies and Account Lockout Policies profiles bound to the vService are listed row by row. |
| Session | The selected Session Protection Policies profile and the sentence that summarizes the validity duration of the session cookie. |
When the information icon on the right of the rows is clicked, the summary of the related profile or setting opens.
Under the cards the end nodes of the flow, in Portal mode the applications bound to the portal and in Portal Application mode the trusted portals are displayed. The two icons below the diagram open the page view and the notification cards.
The diagram is read-only on this screen
The information icons in the diagram only show the detail of the related setting. Editing is done from the AGS Management and Flowchart tabs on the vService screen.
Scope and Limits
INFO
- The screen depends on the AGS license; for the details the Products & Licensing page must be consulted.
- The screen depends on the Load Balancer permission area; for a user who does not have the permission the You don't have access to this page card is displayed instead of the page.
- A user who has read-only permission sees the list; the Edit operation is not shown in the preview, while the Enable and Disable buttons in the toolbar and the right-click operations are not hidden.
- An account whose vService scope is limited sees only the vServices defined for it in the list and in the access control starting field.
- The AGS turning on and removing operations do not write a separate record into the log timeline in the preview; the trace of the change stays in the configuration itself.
- The list is updated automatically as the configuration changes; a separate refresh step is not required. When the operating mode or the flow of a vService is changed on the AGS Management screen, the row and the preview diagram show the new value immediately.
- The vService life cycle is not managed on this screen; deleting, stopping, starting and reloading are done from the Load Balancer vService list.
